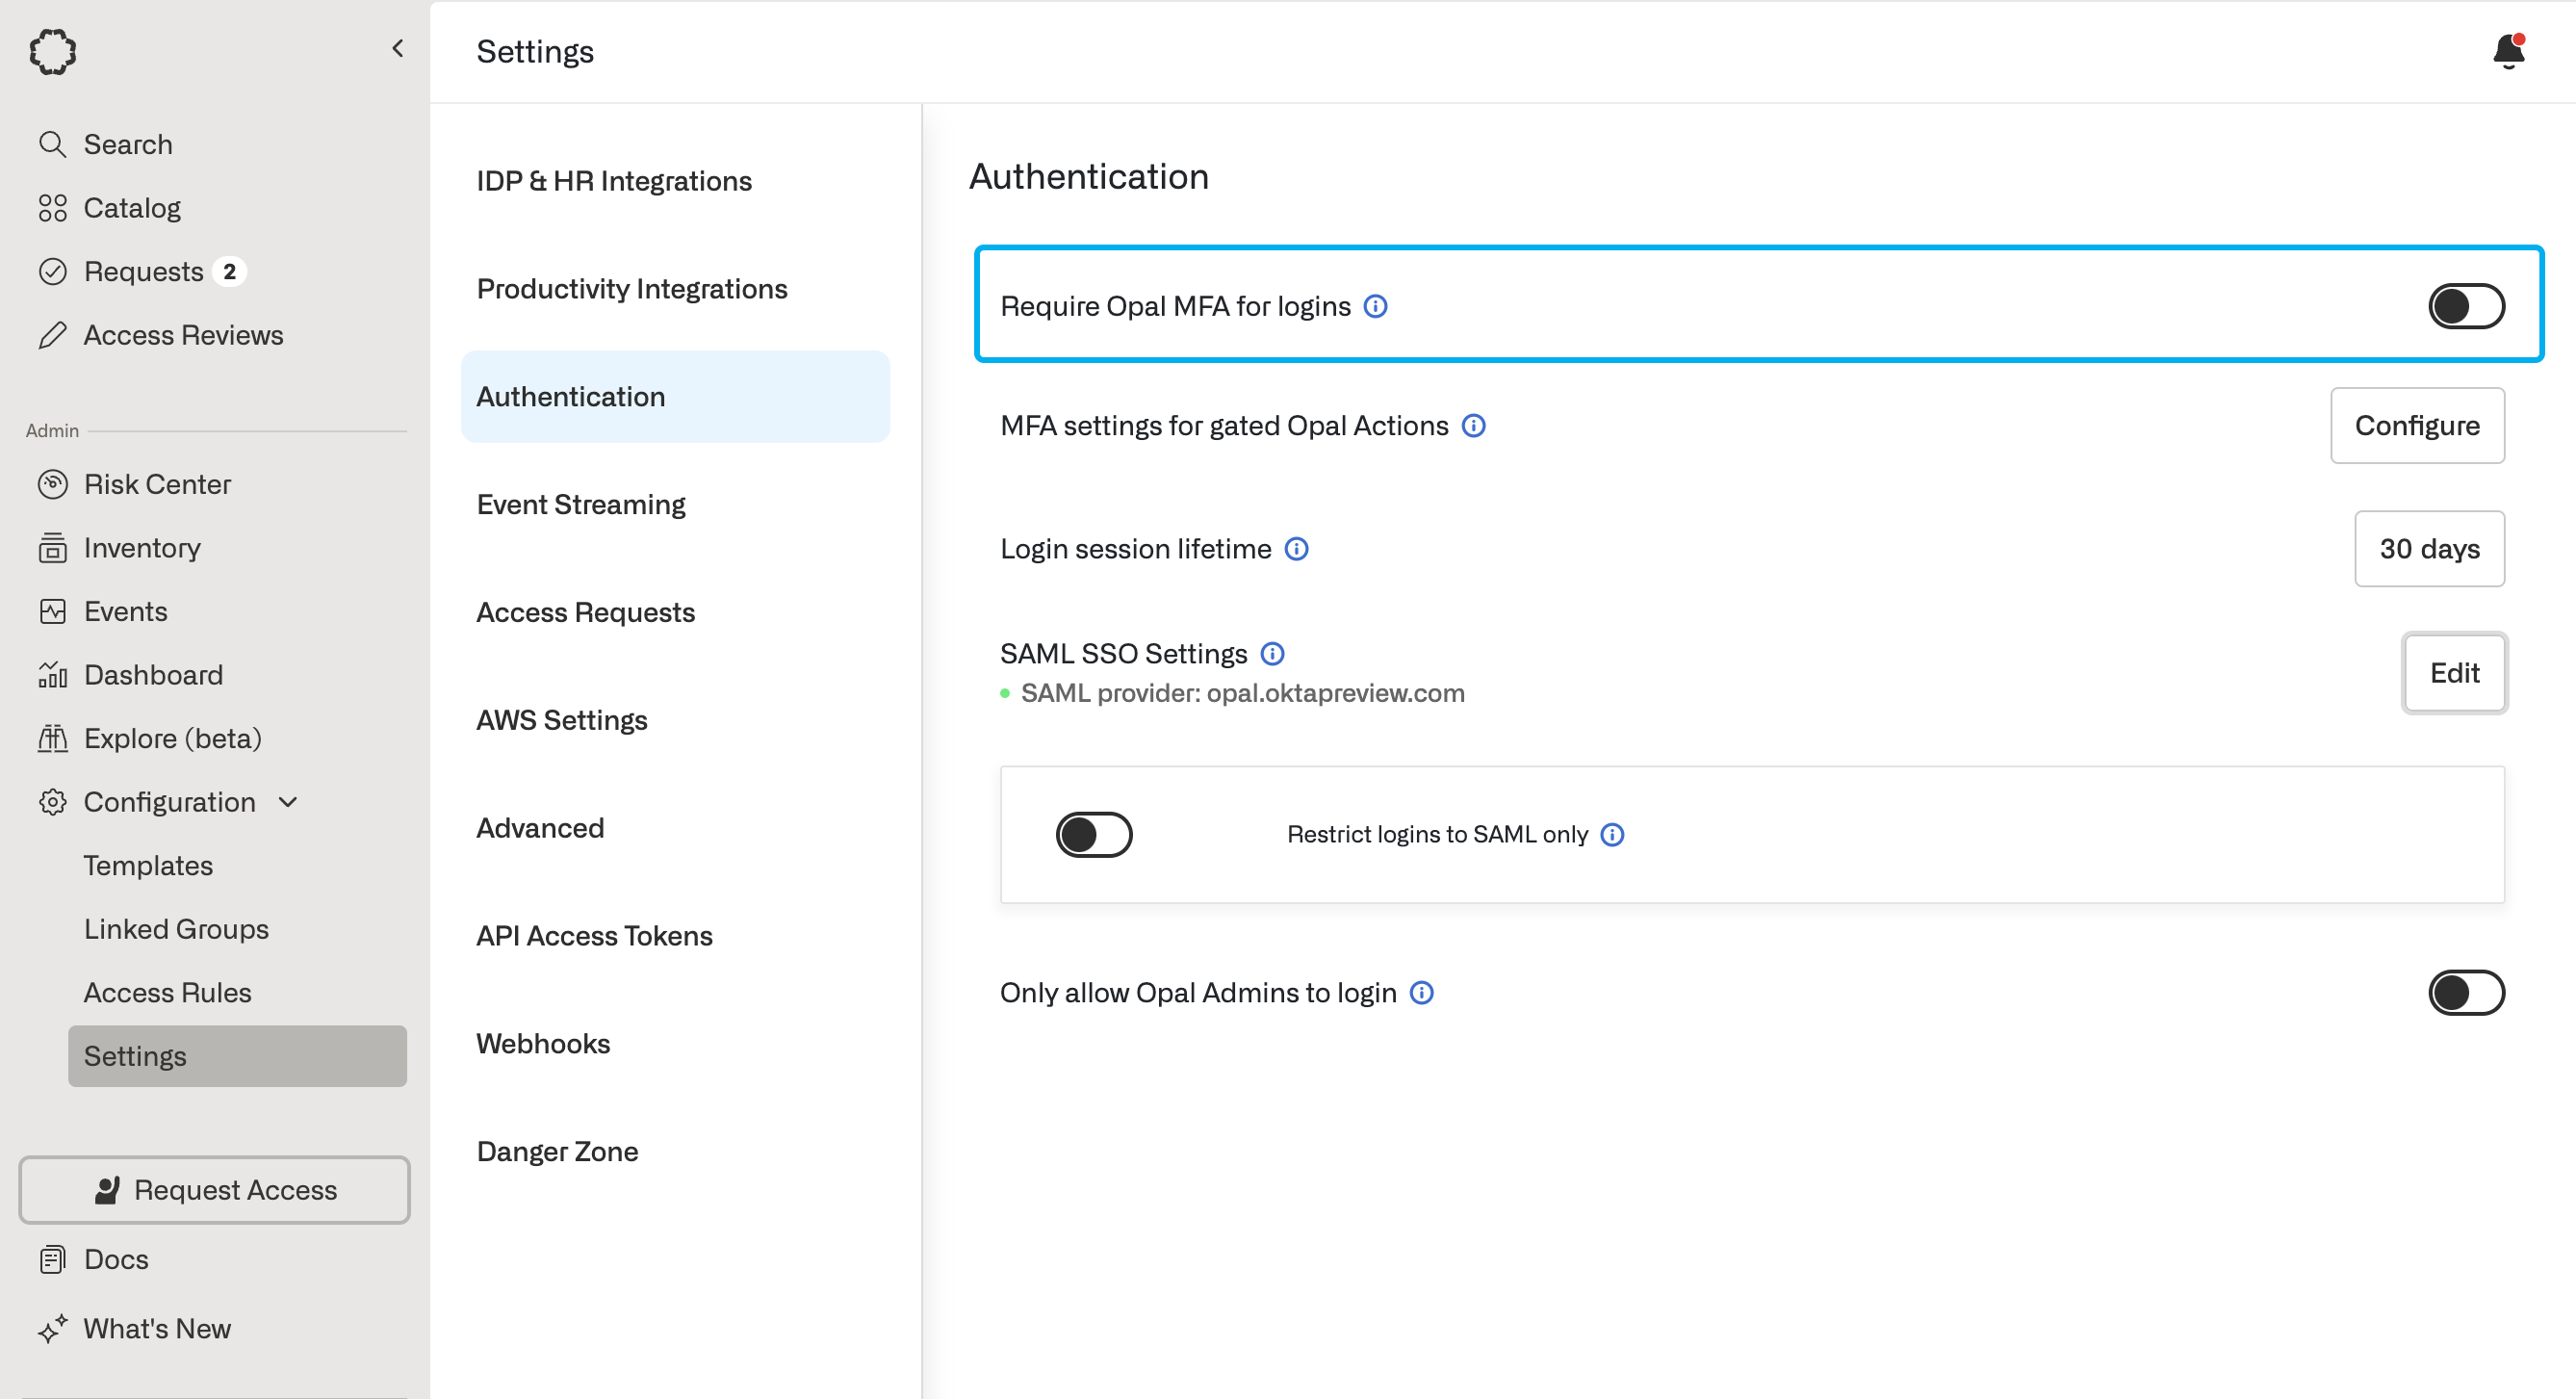
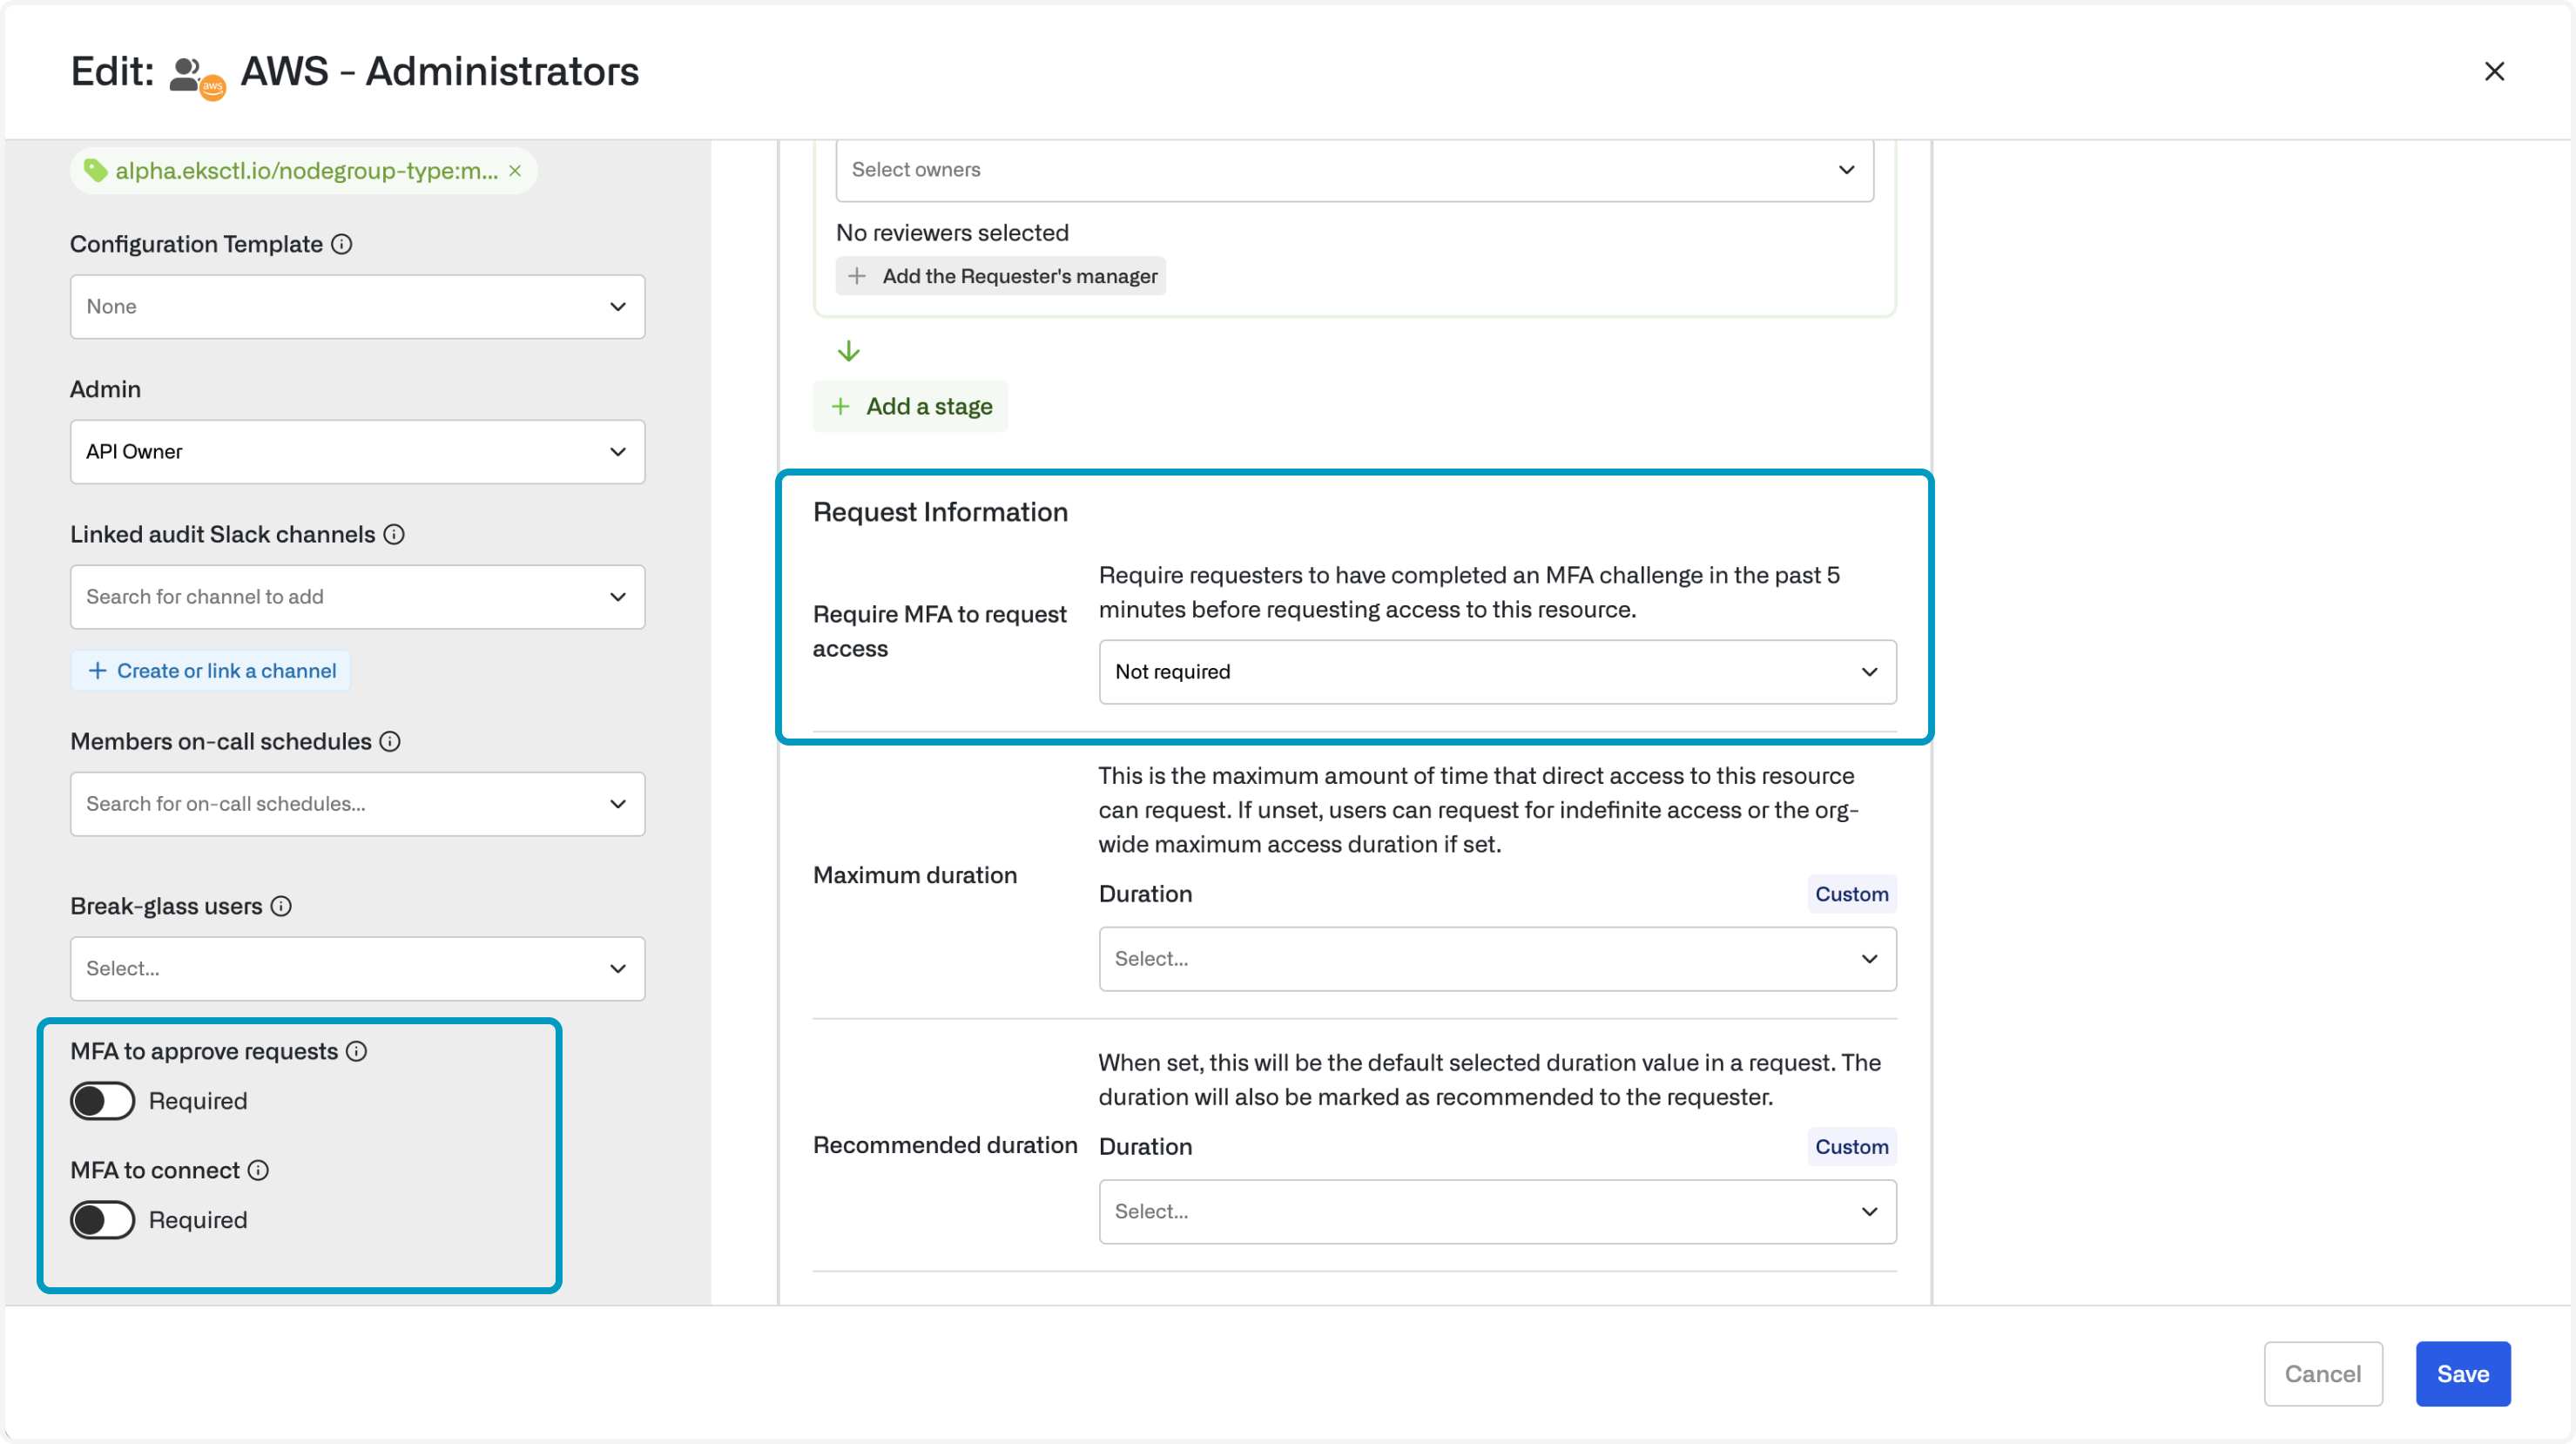
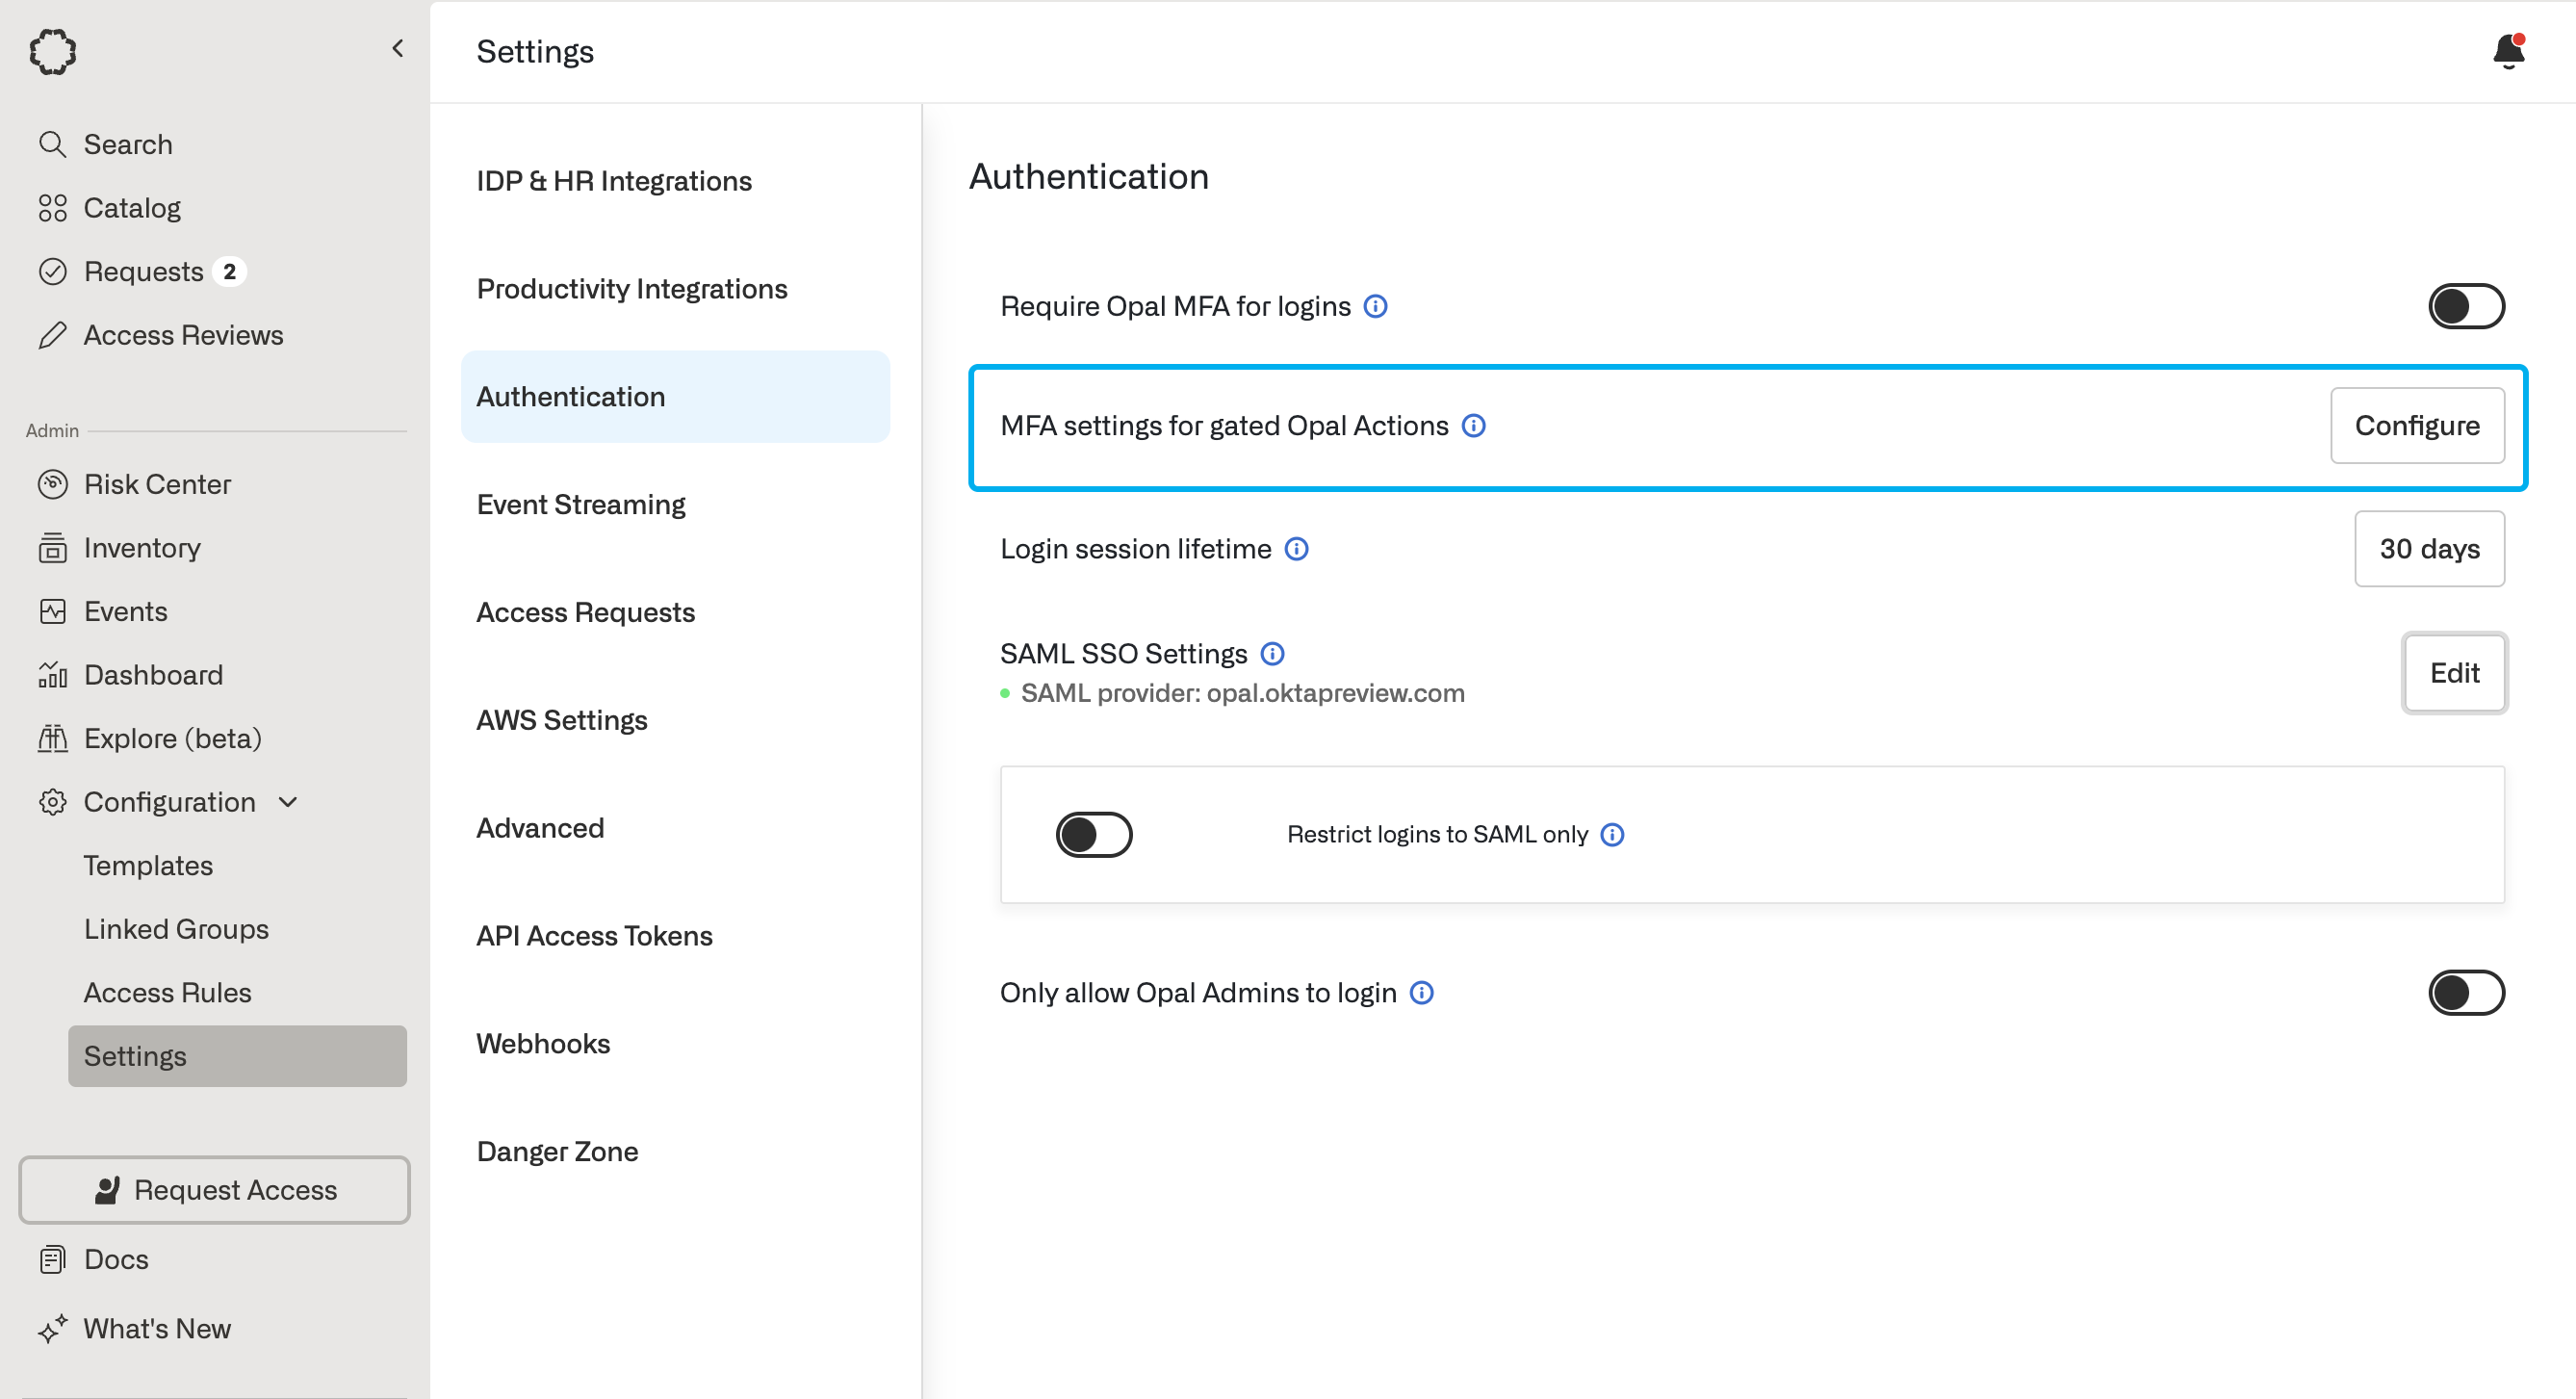
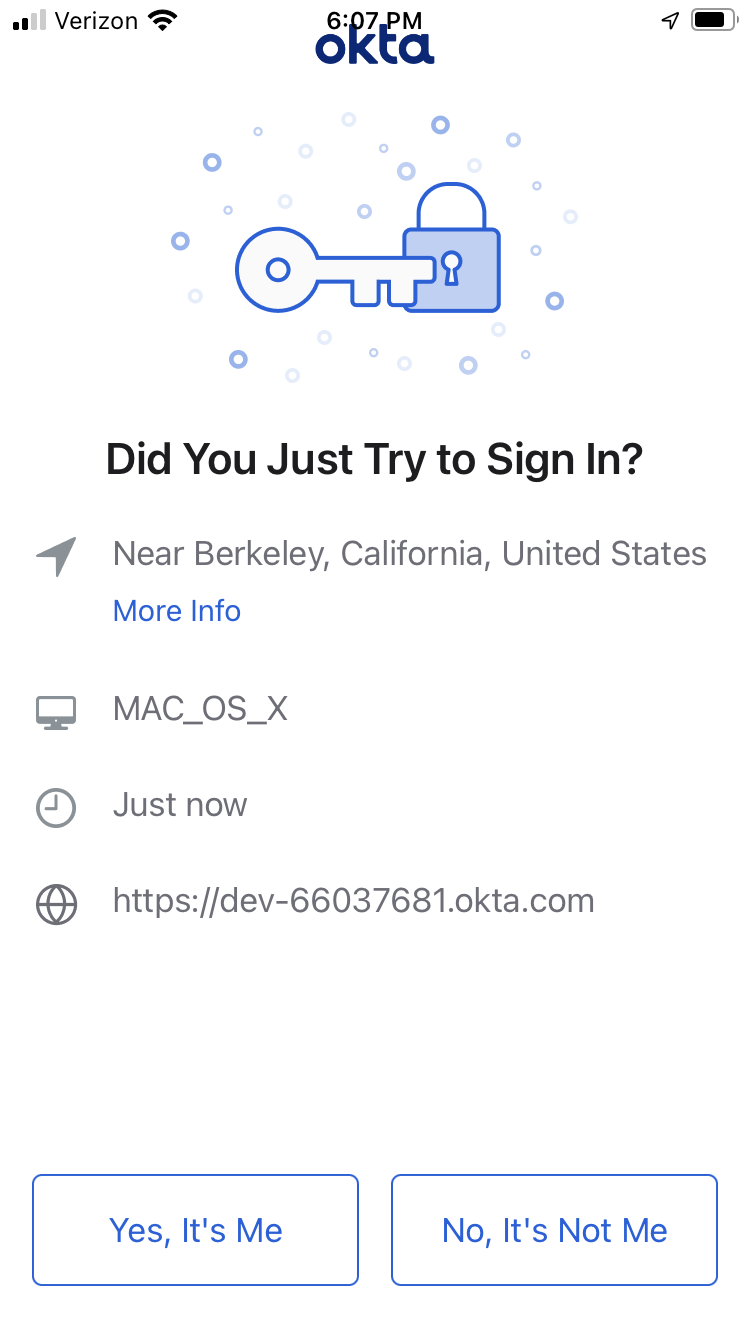
When a push notification is sent to the Okta Verify app, the location associated with the user agent is included to prevent phishing. Here is an example:Opal’s IP ranges must be added to the allowlist in your org’s network security settings as a trusted proxy to forward the user agent’s original IP address with the X-Forwarded-For HTTP header.Note: If running Opal self-hosted, please use the public IP ranges for your infrastructure.Navigate to the Configuration section in Okta:
Under Security, click Networks.
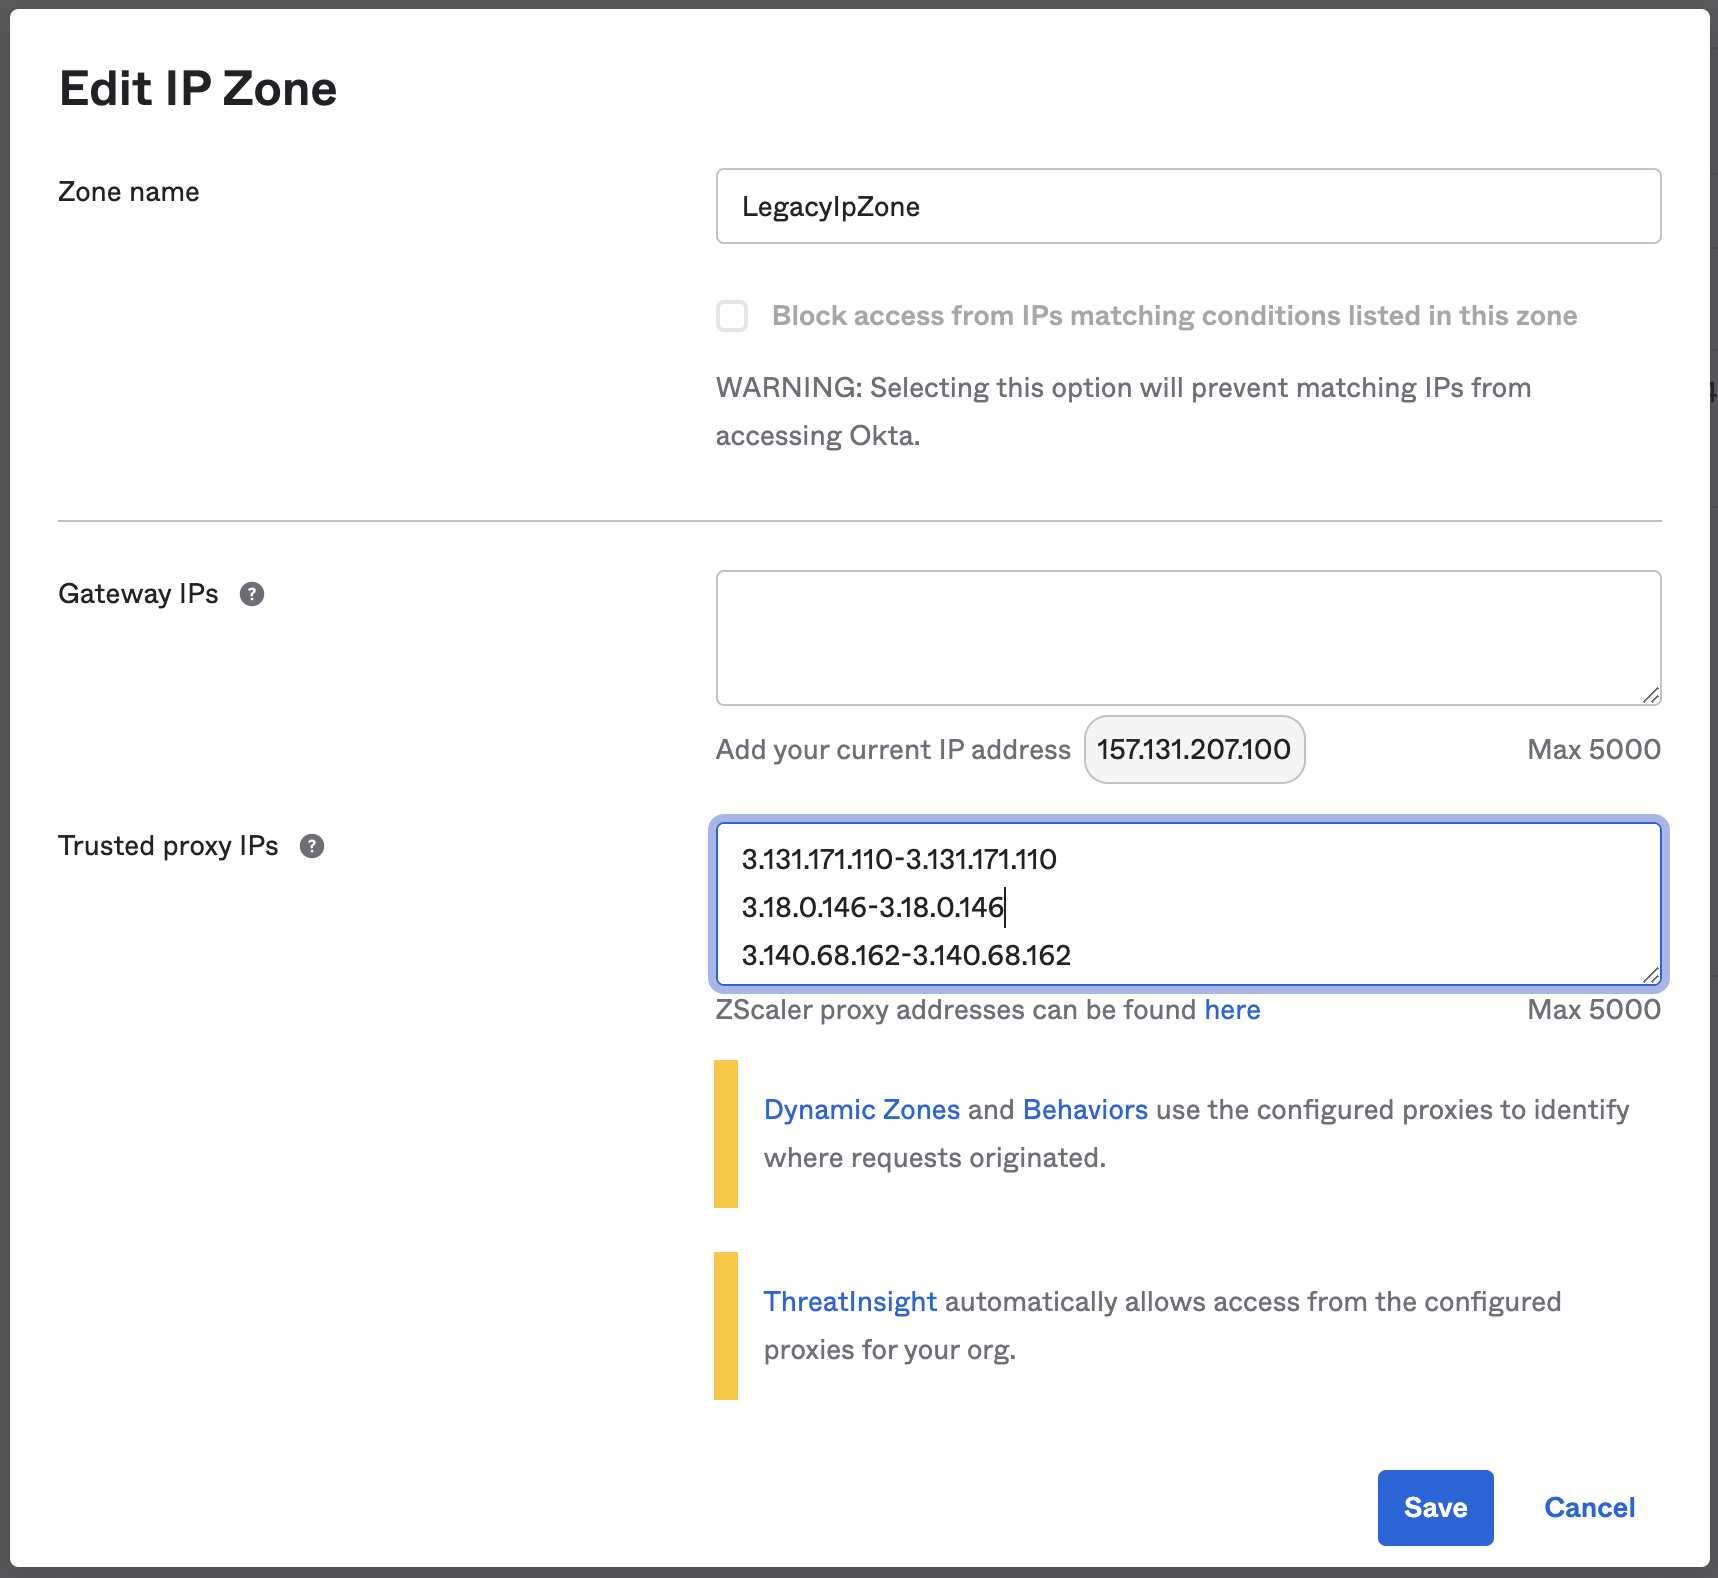
Edit the allowlist IP zone.
Add the IP ranges under Trusted proxy IPs, like so:
Last modified on October 20, 2025
Was this page helpful?
Assistant
Responses are generated using AI and may contain mistakes.