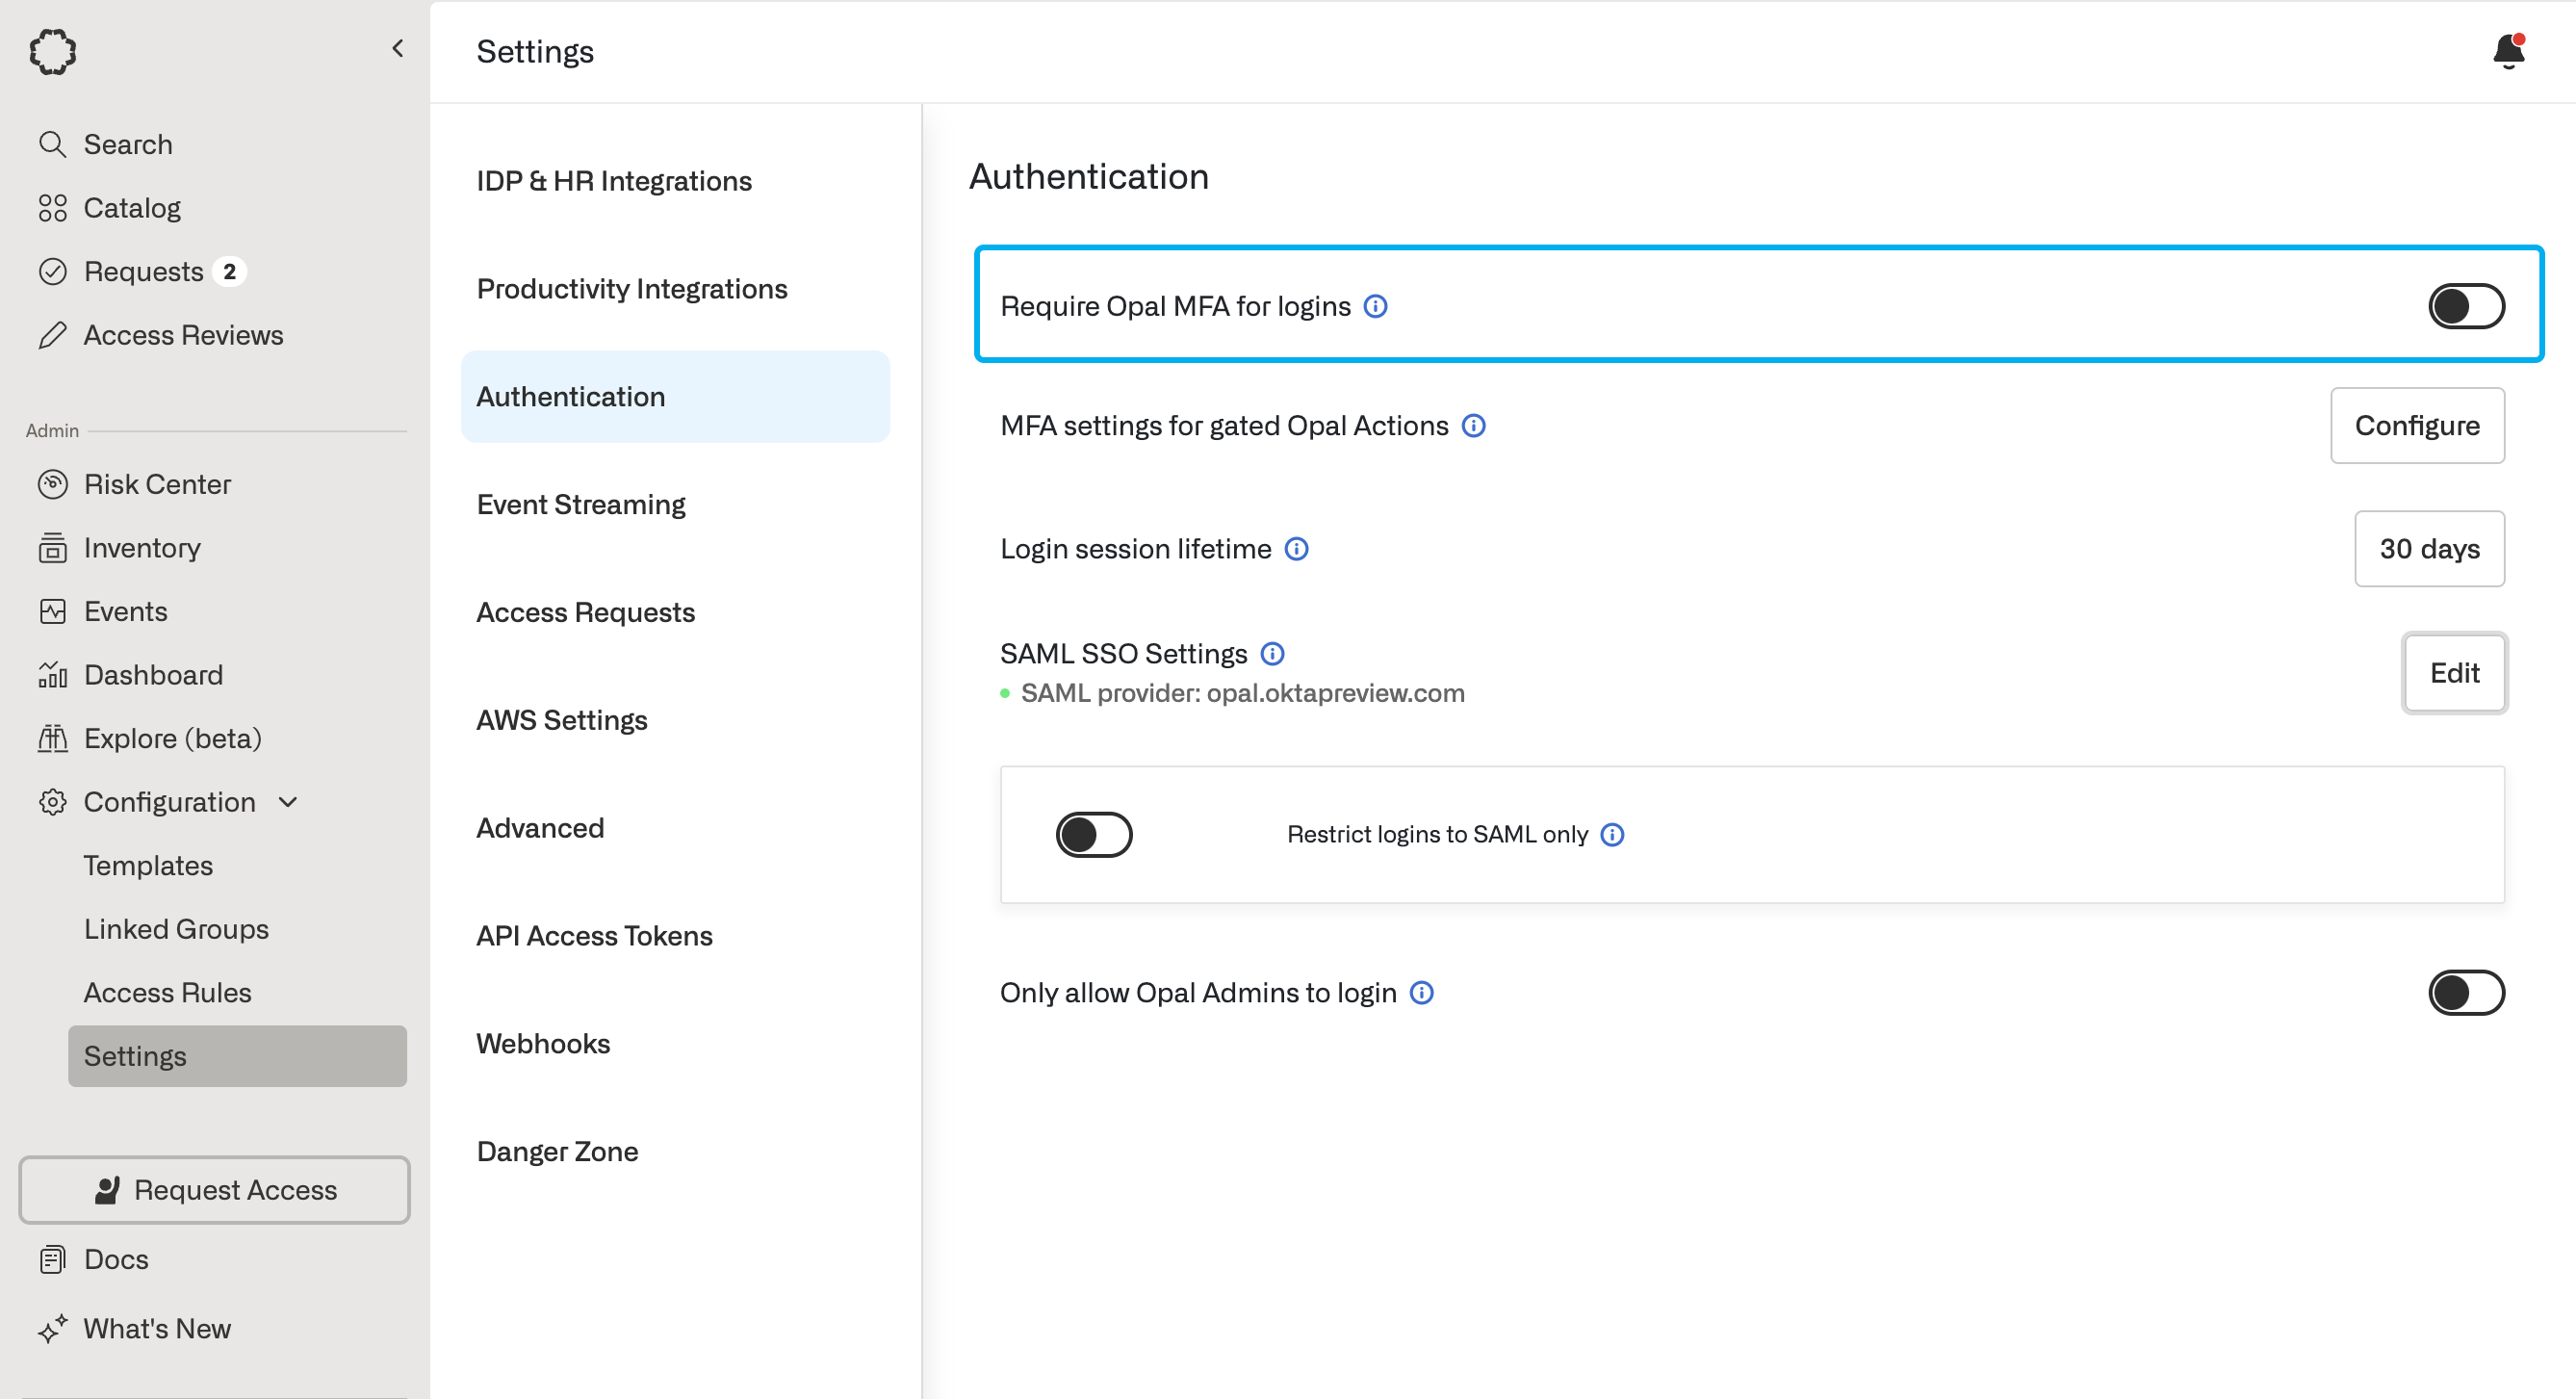
Toggle the Require Opal MFA for logins setting to enable Opal-managed MFA.Alternatively, you can enable MFA through your SAML provider. In this case, disable this setting. See the Okta multifactor authentication guide for more detail on the Okta configuration.
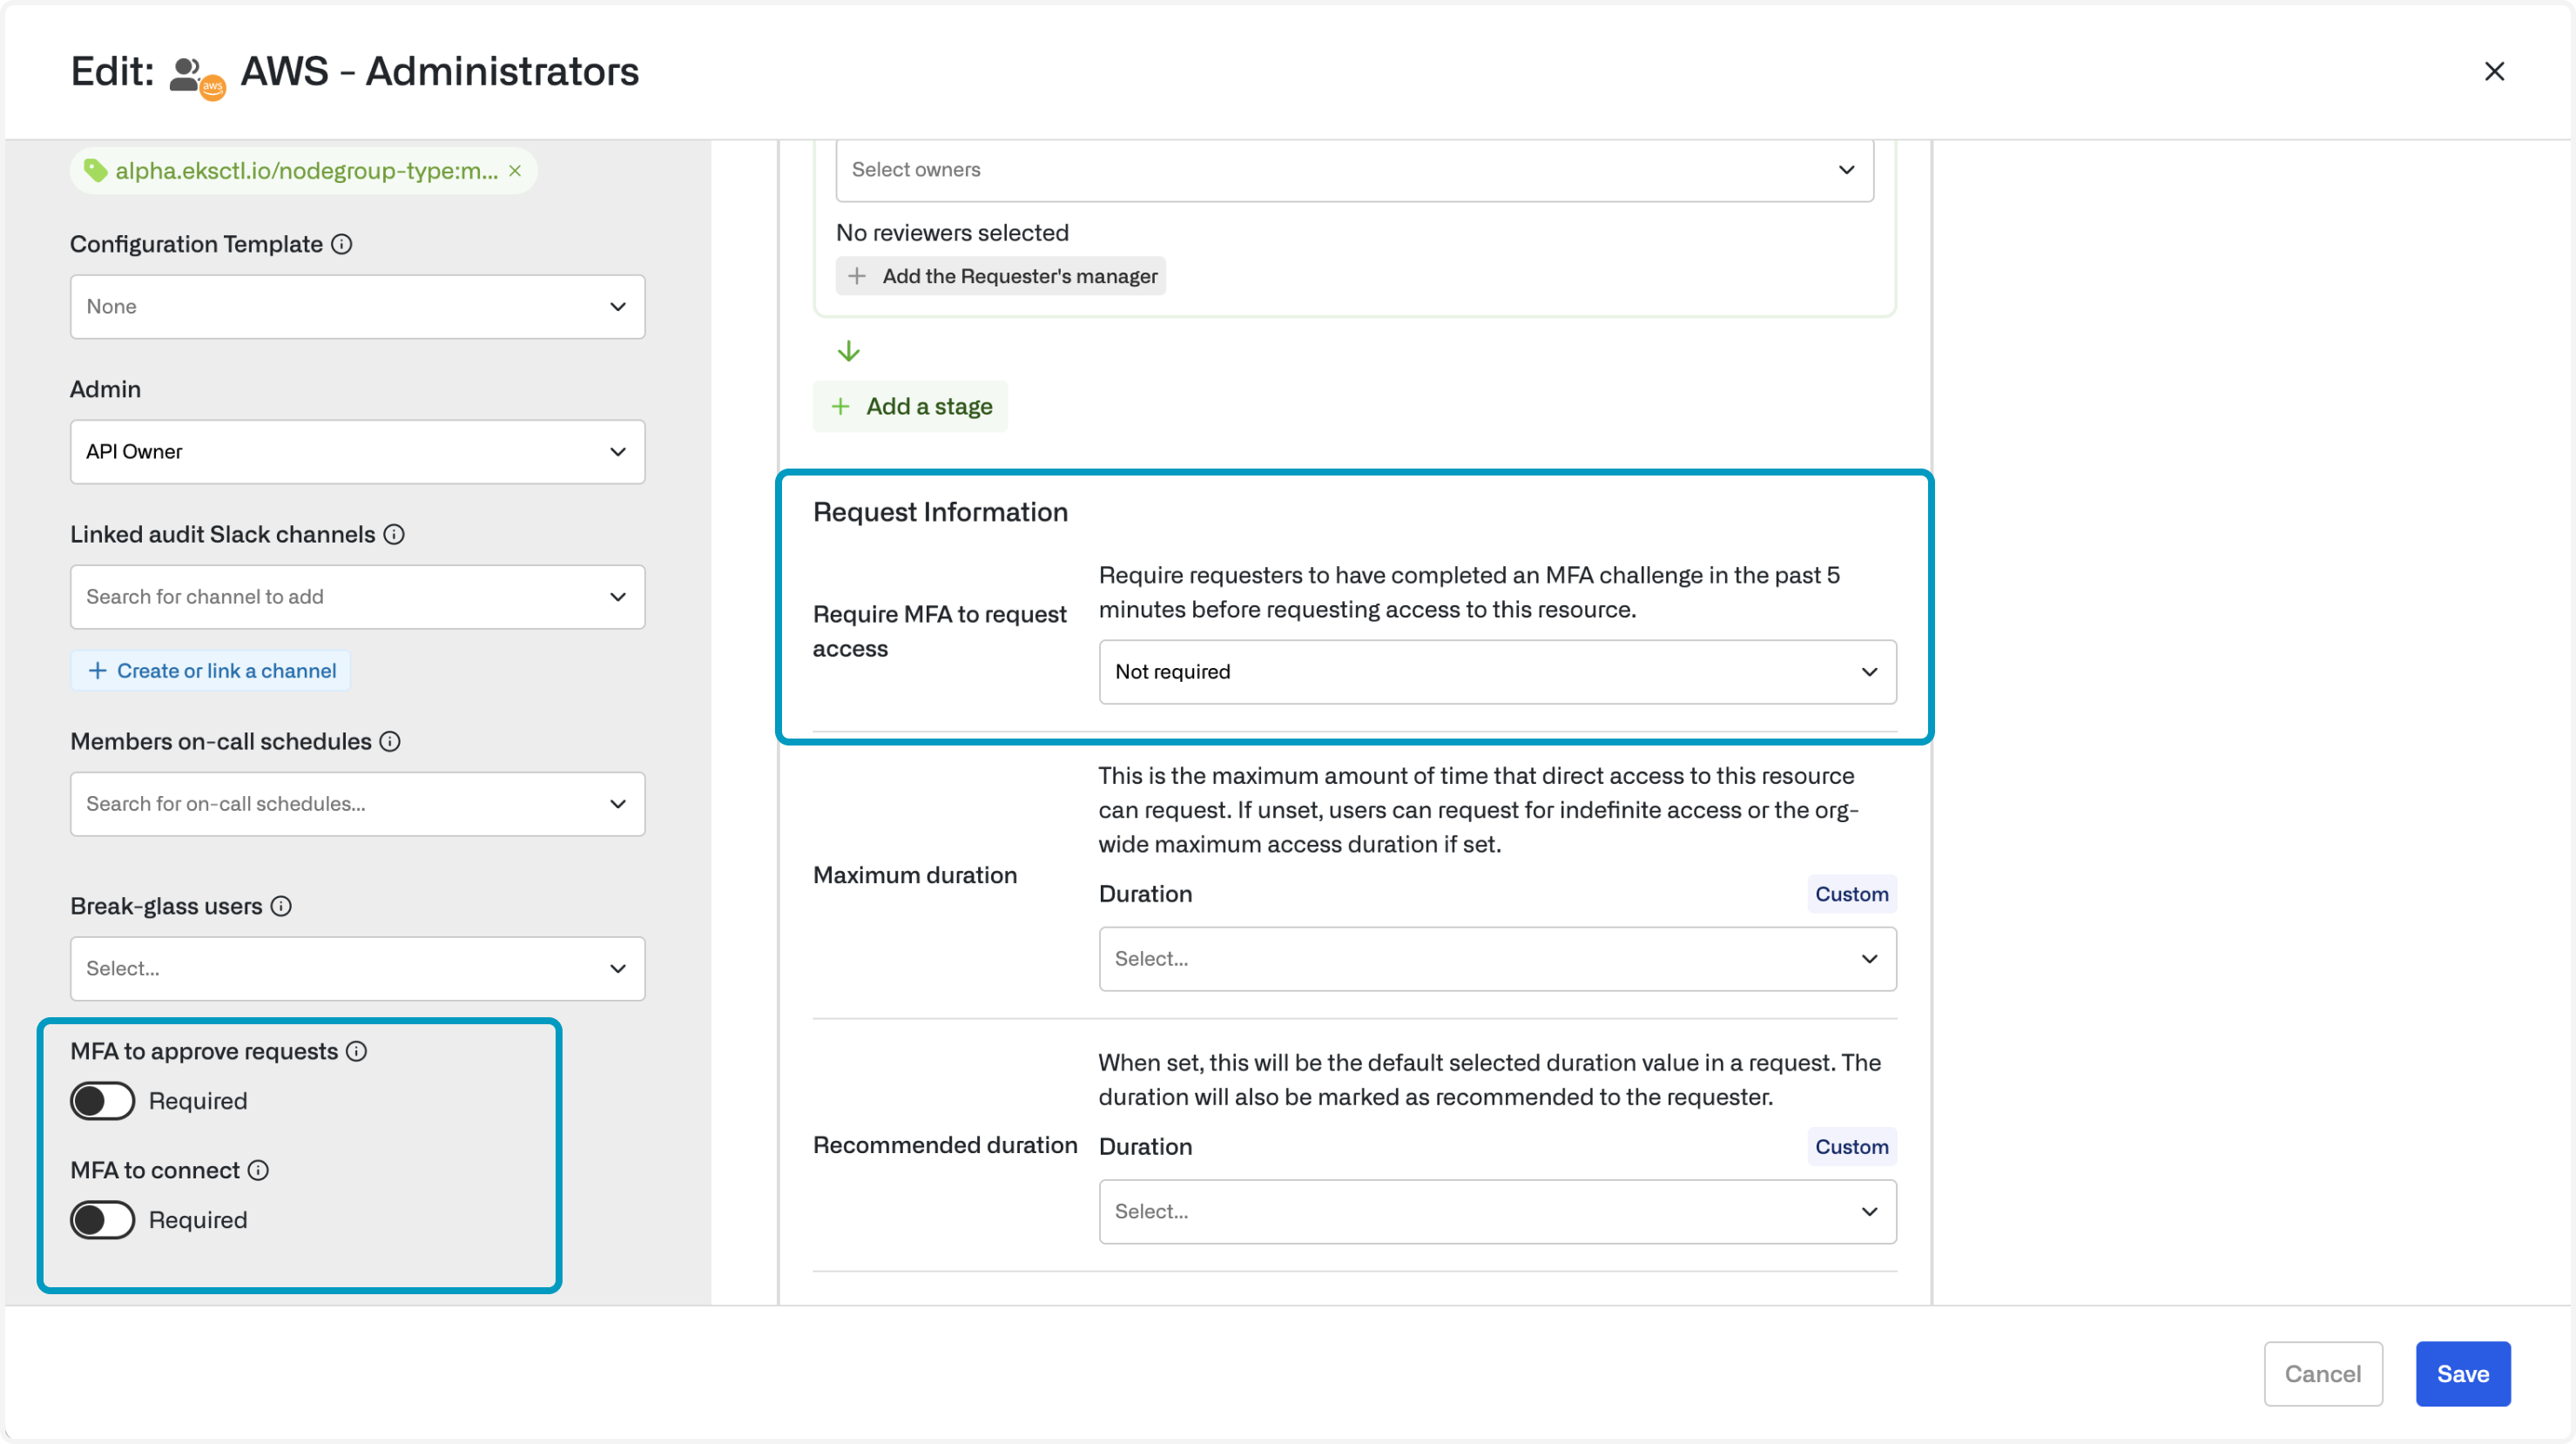
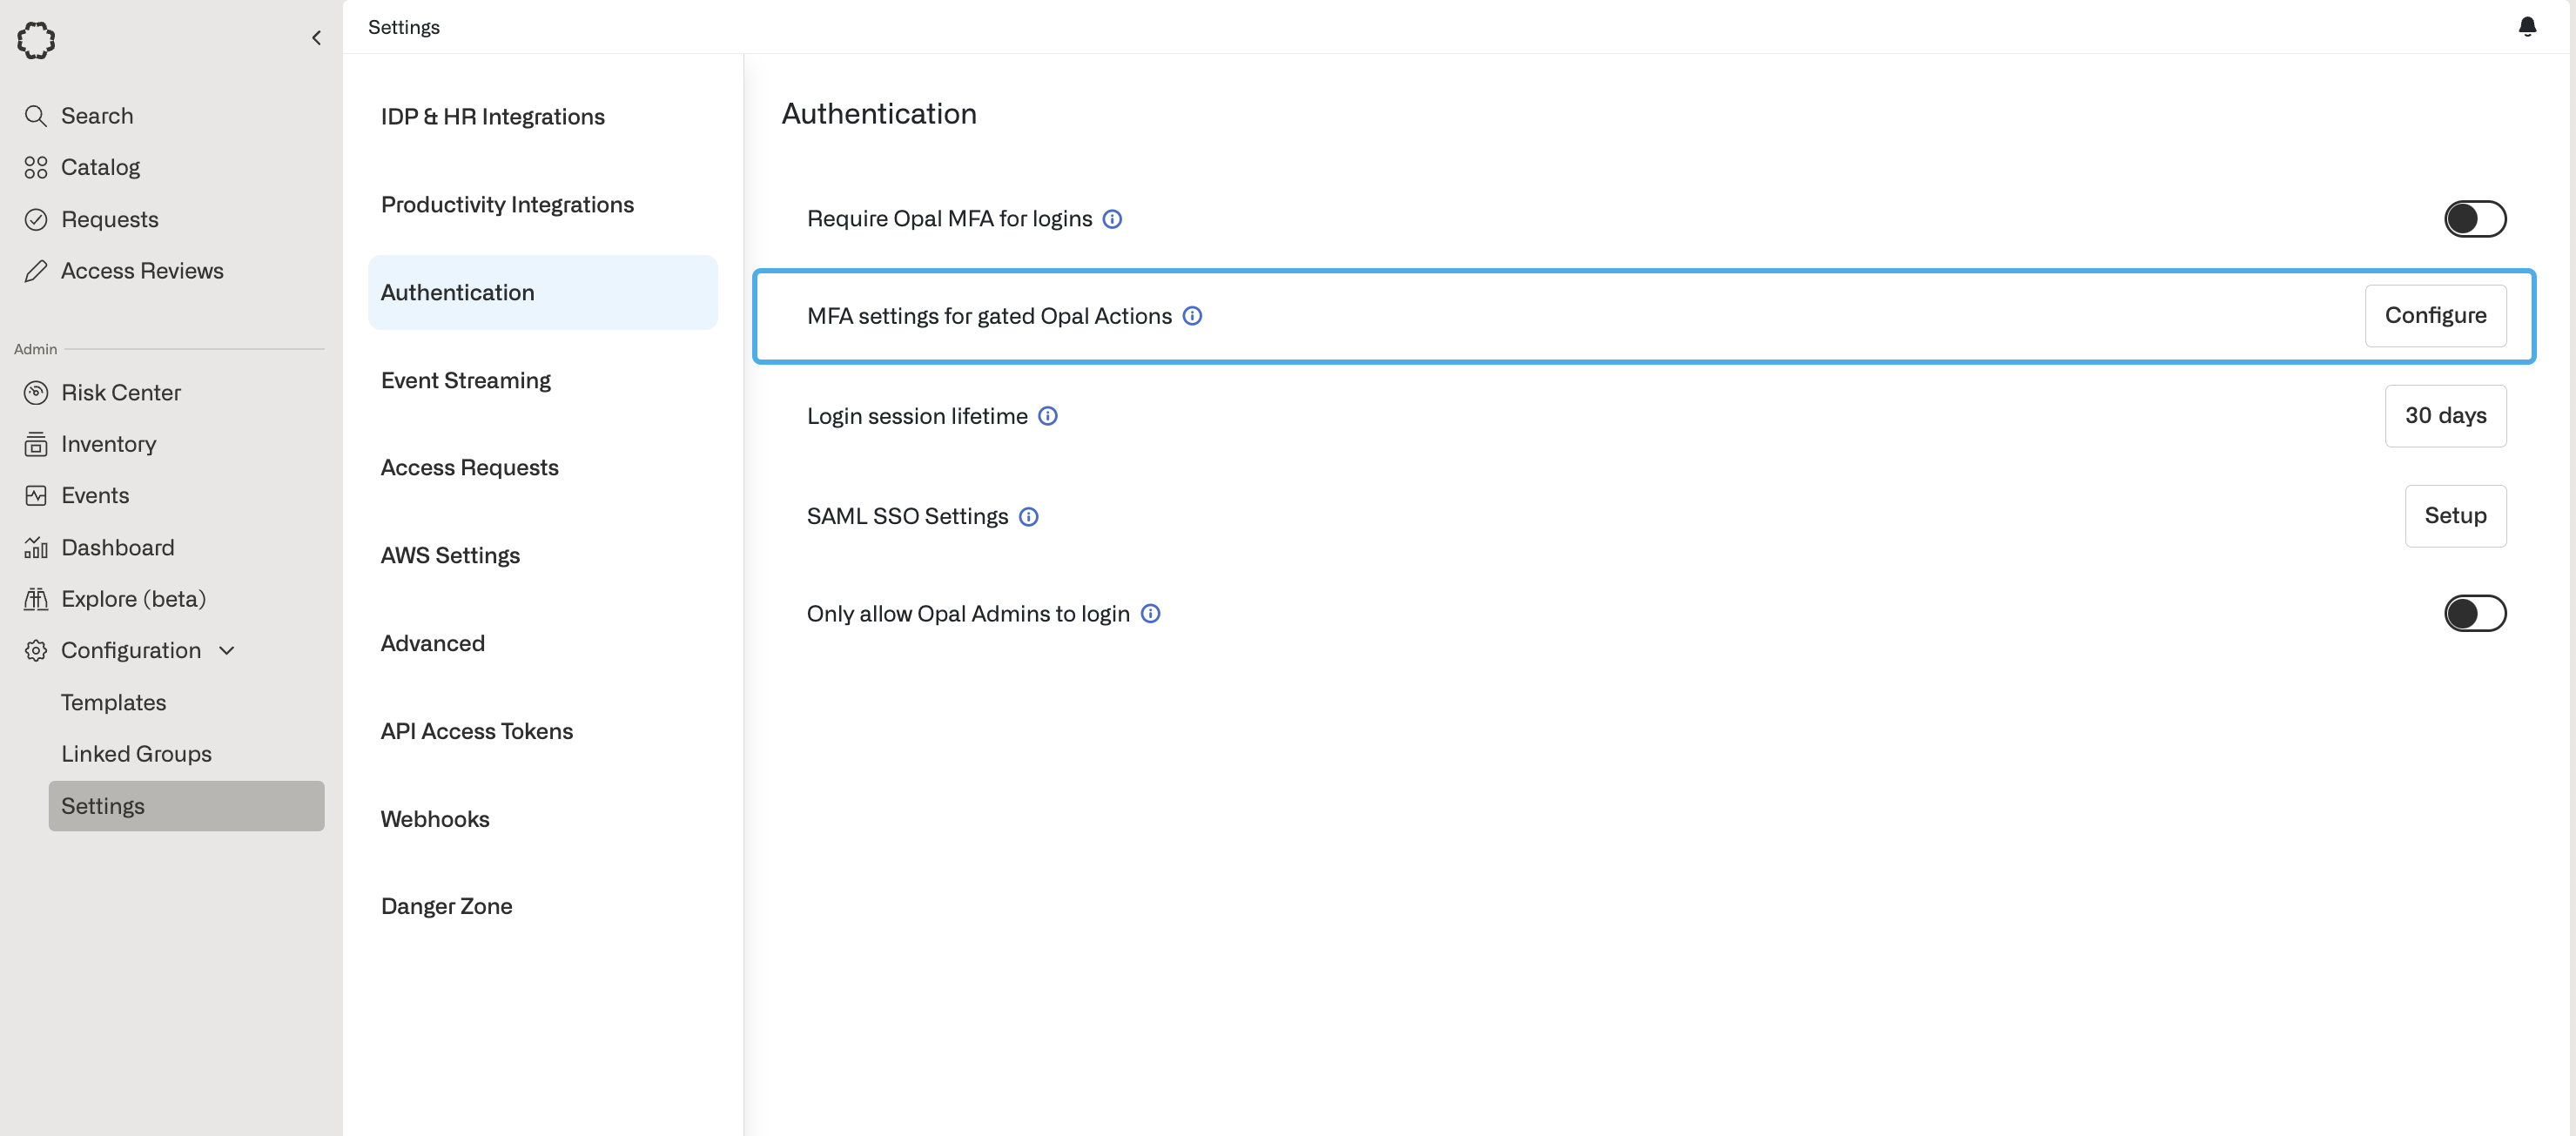
MFA for Opal actions can be toggled on a per-action, per-resource level. Edit your resource to enable MFA.To modify your MFA Provider settings for Opal Actions, go to Configuration > Settings > Authentication and select Configure next to MFA settings for gated Opal Actions.Three different options for MFA providers are supported:
Opal managed MFA: Users can register their MFA devices through Opal.
OIDC MFA: Opal supports any OIDC provider, including Okta and Azure, as a MFA solution. Once configured, users will be able to use any MFA method that your OIDC provider supports, including WebAuthn (Yubikey, TouchID, etc.) and TOTP.
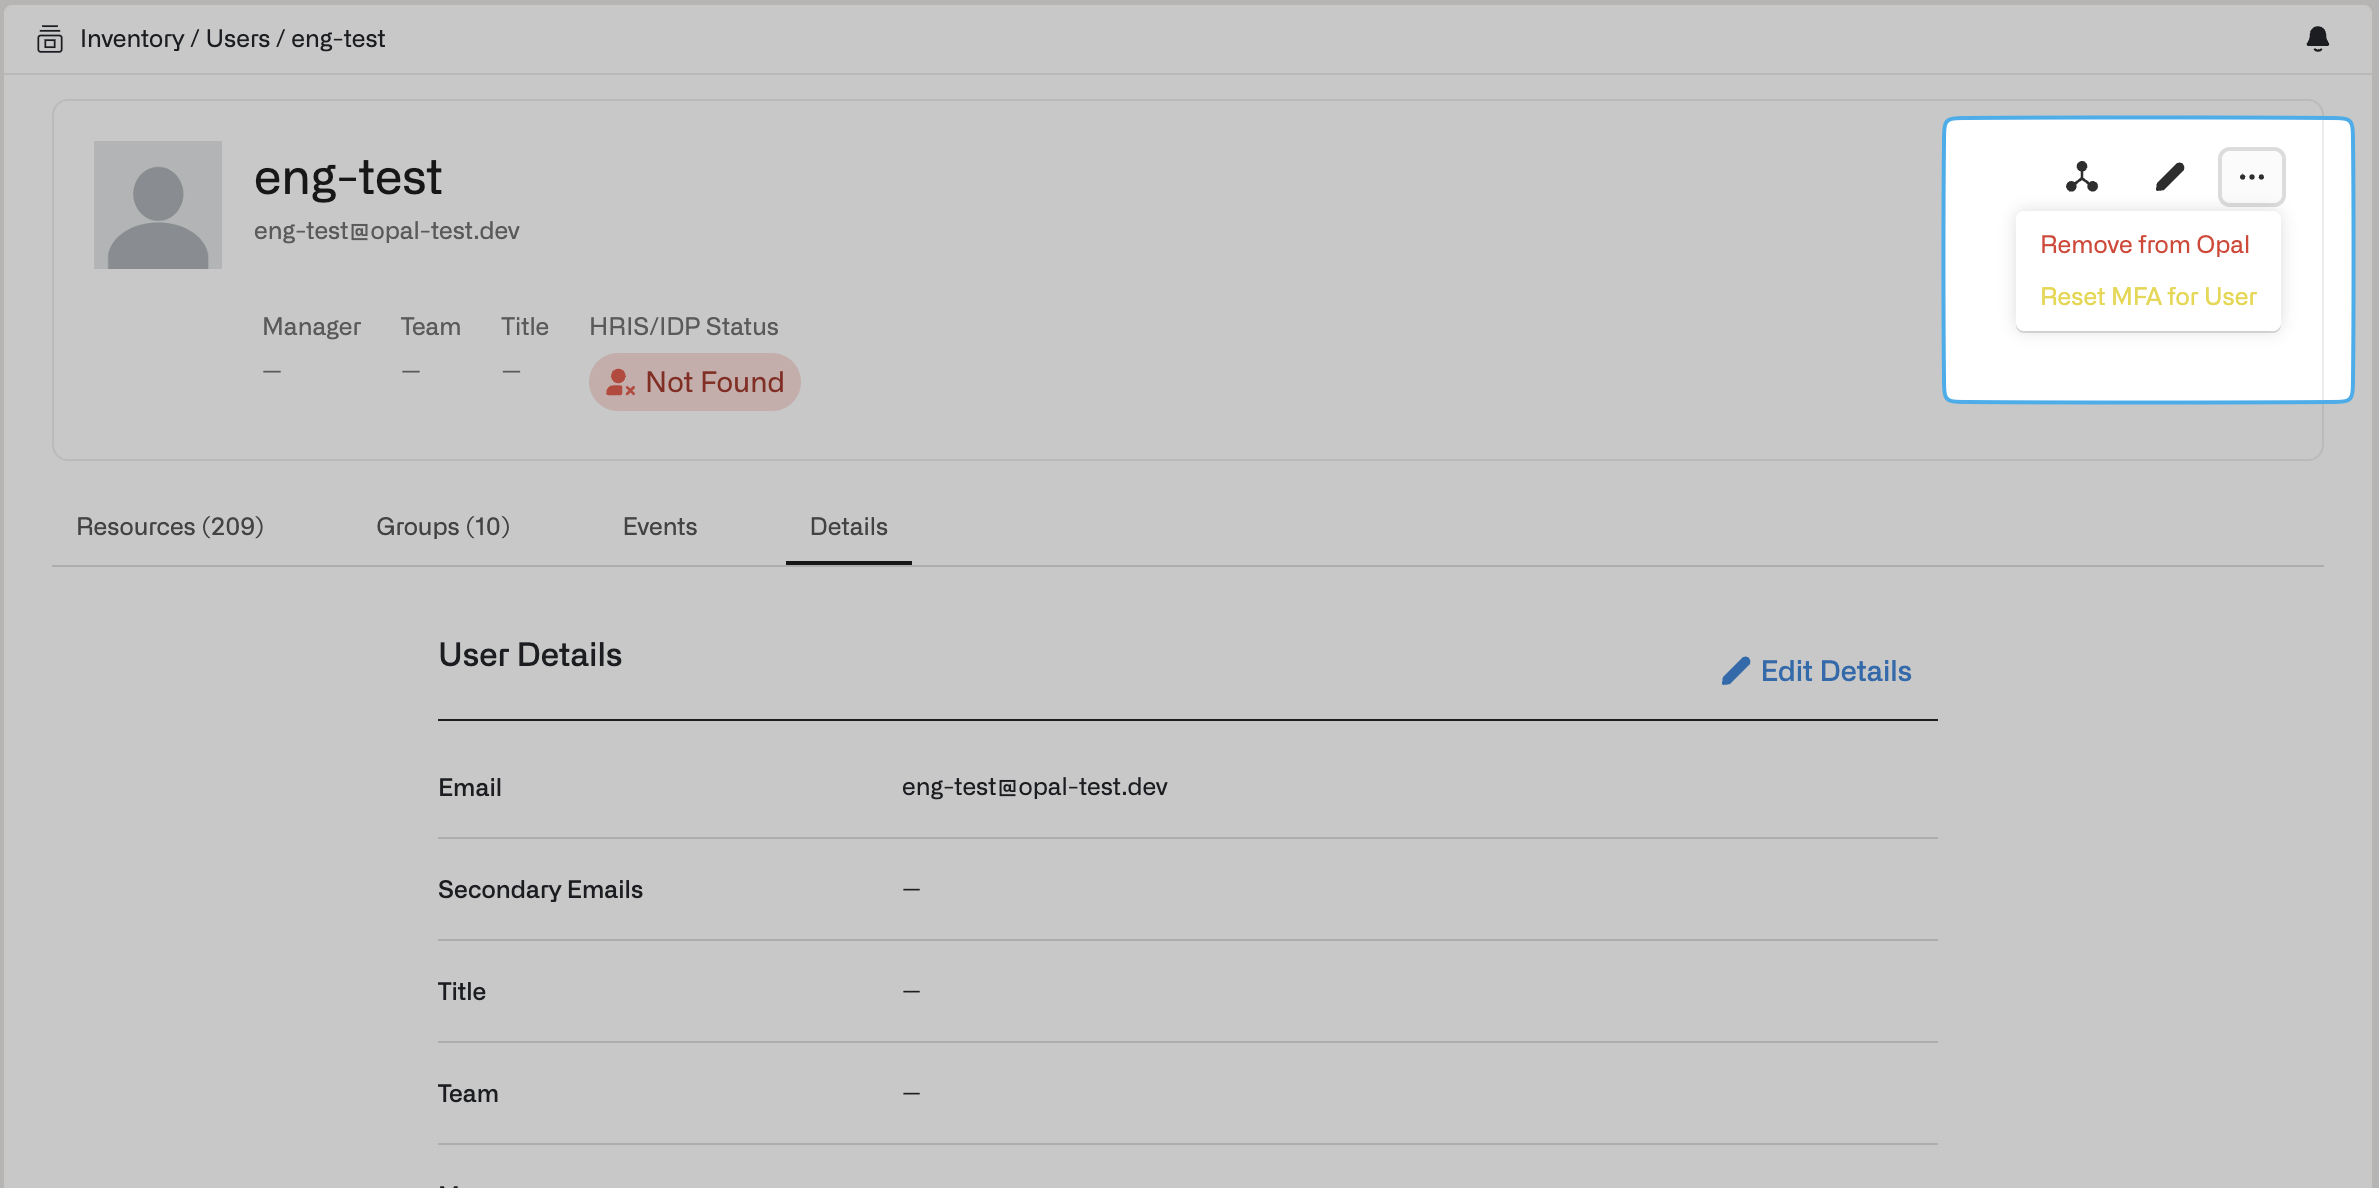
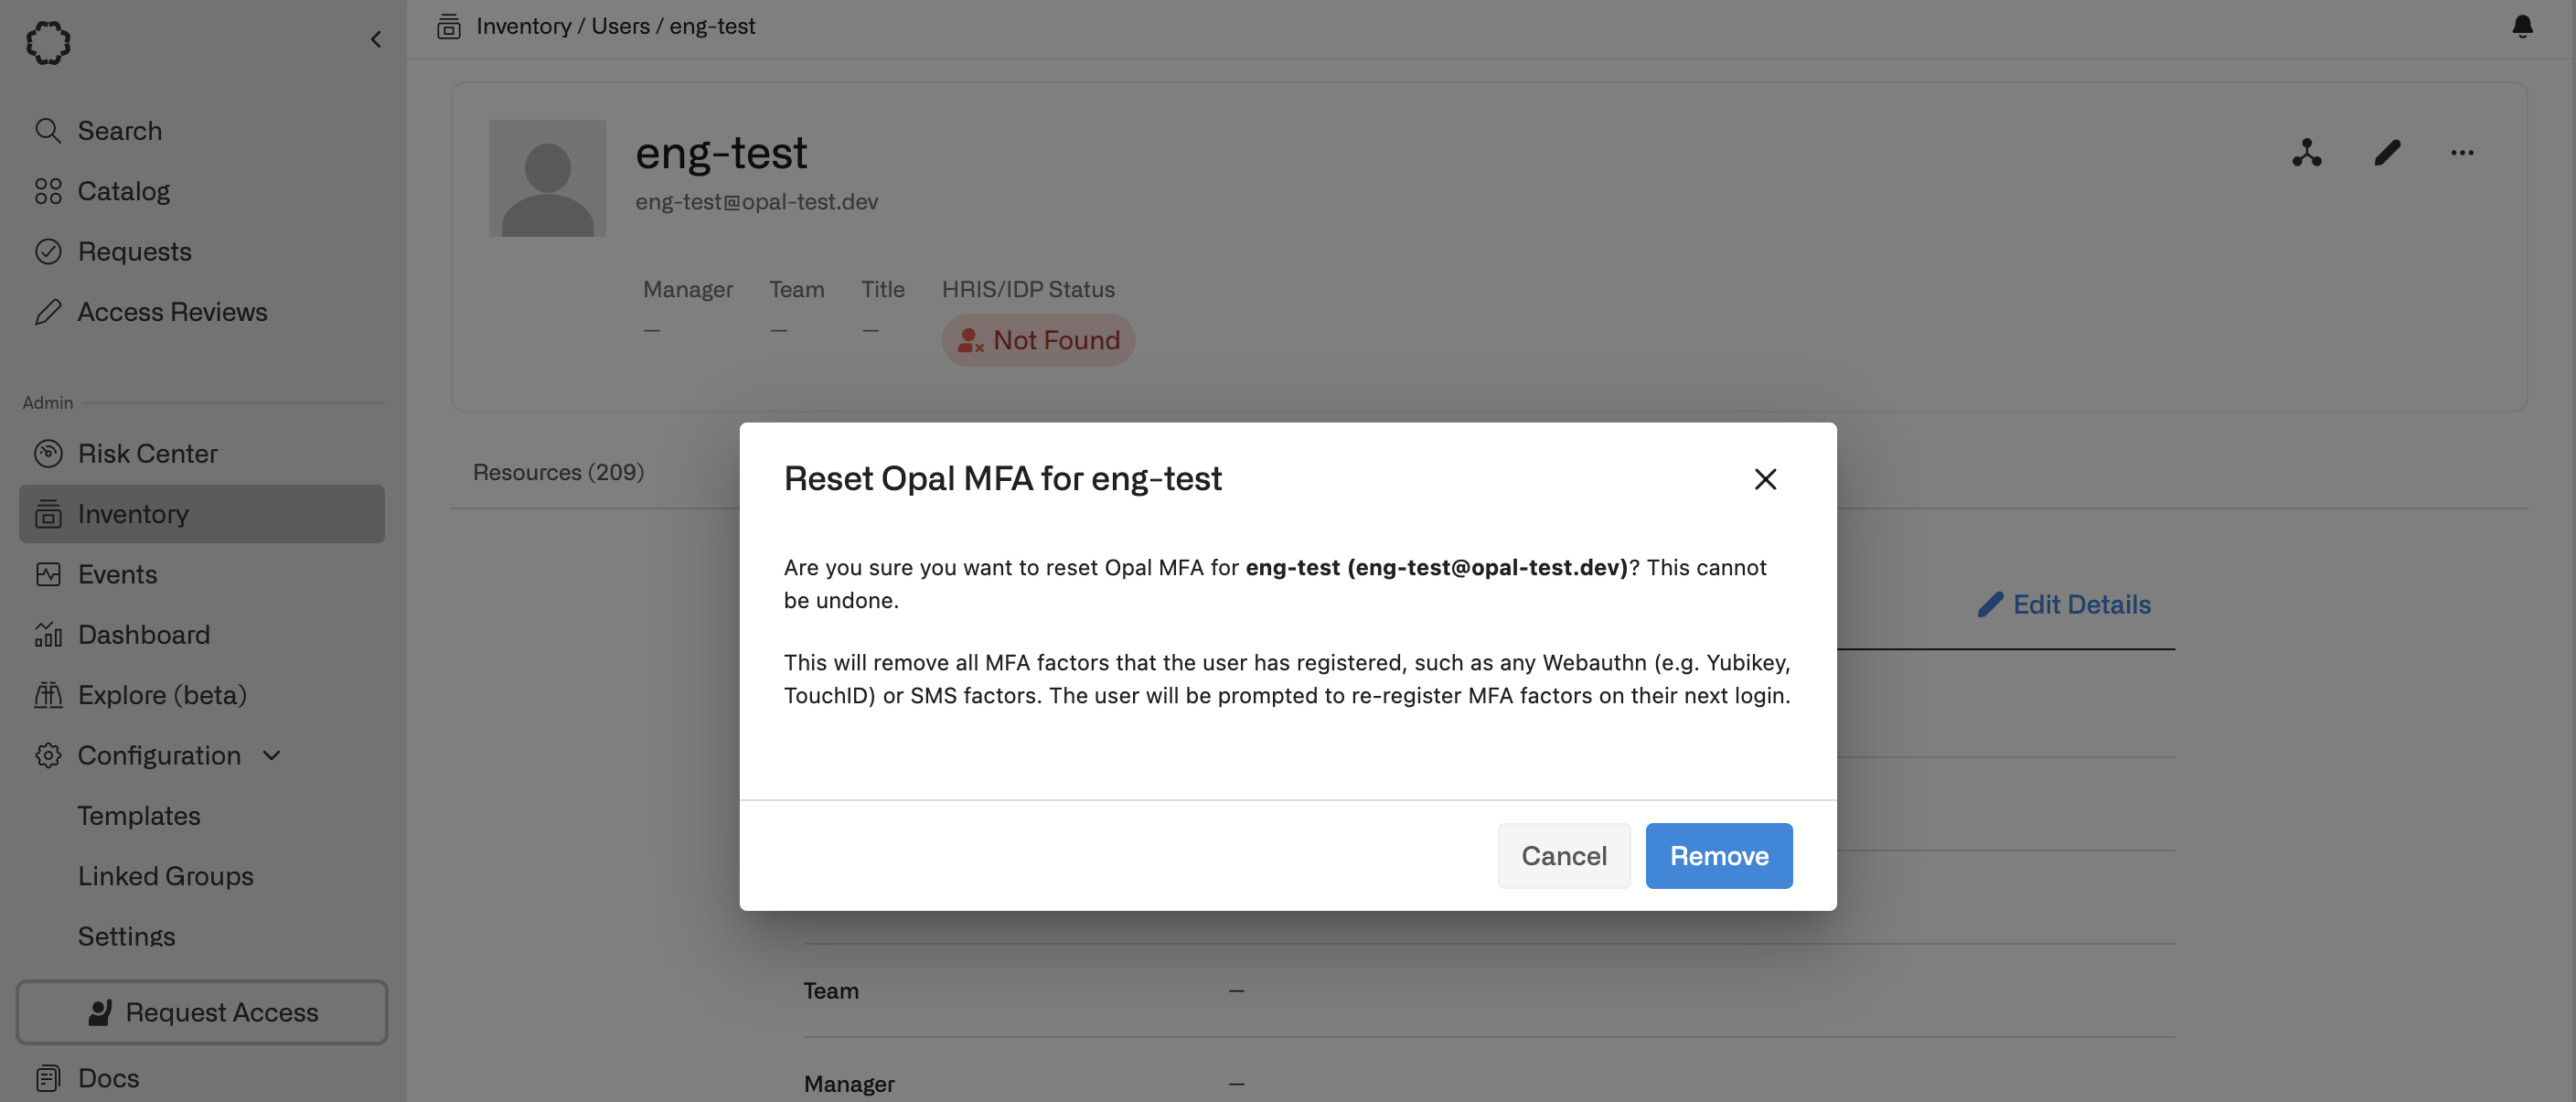
To reset MFA for an individual user, go to the Inventory > Users tab, then find the user detail page. Select the … dropdown on the upper right, then Reset MFA for User.Follow the confirmation modal to finish resetting the user’s MFA.
Last modified on October 21, 2025
Was this page helpful?
Assistant
Responses are generated using AI and may contain mistakes.