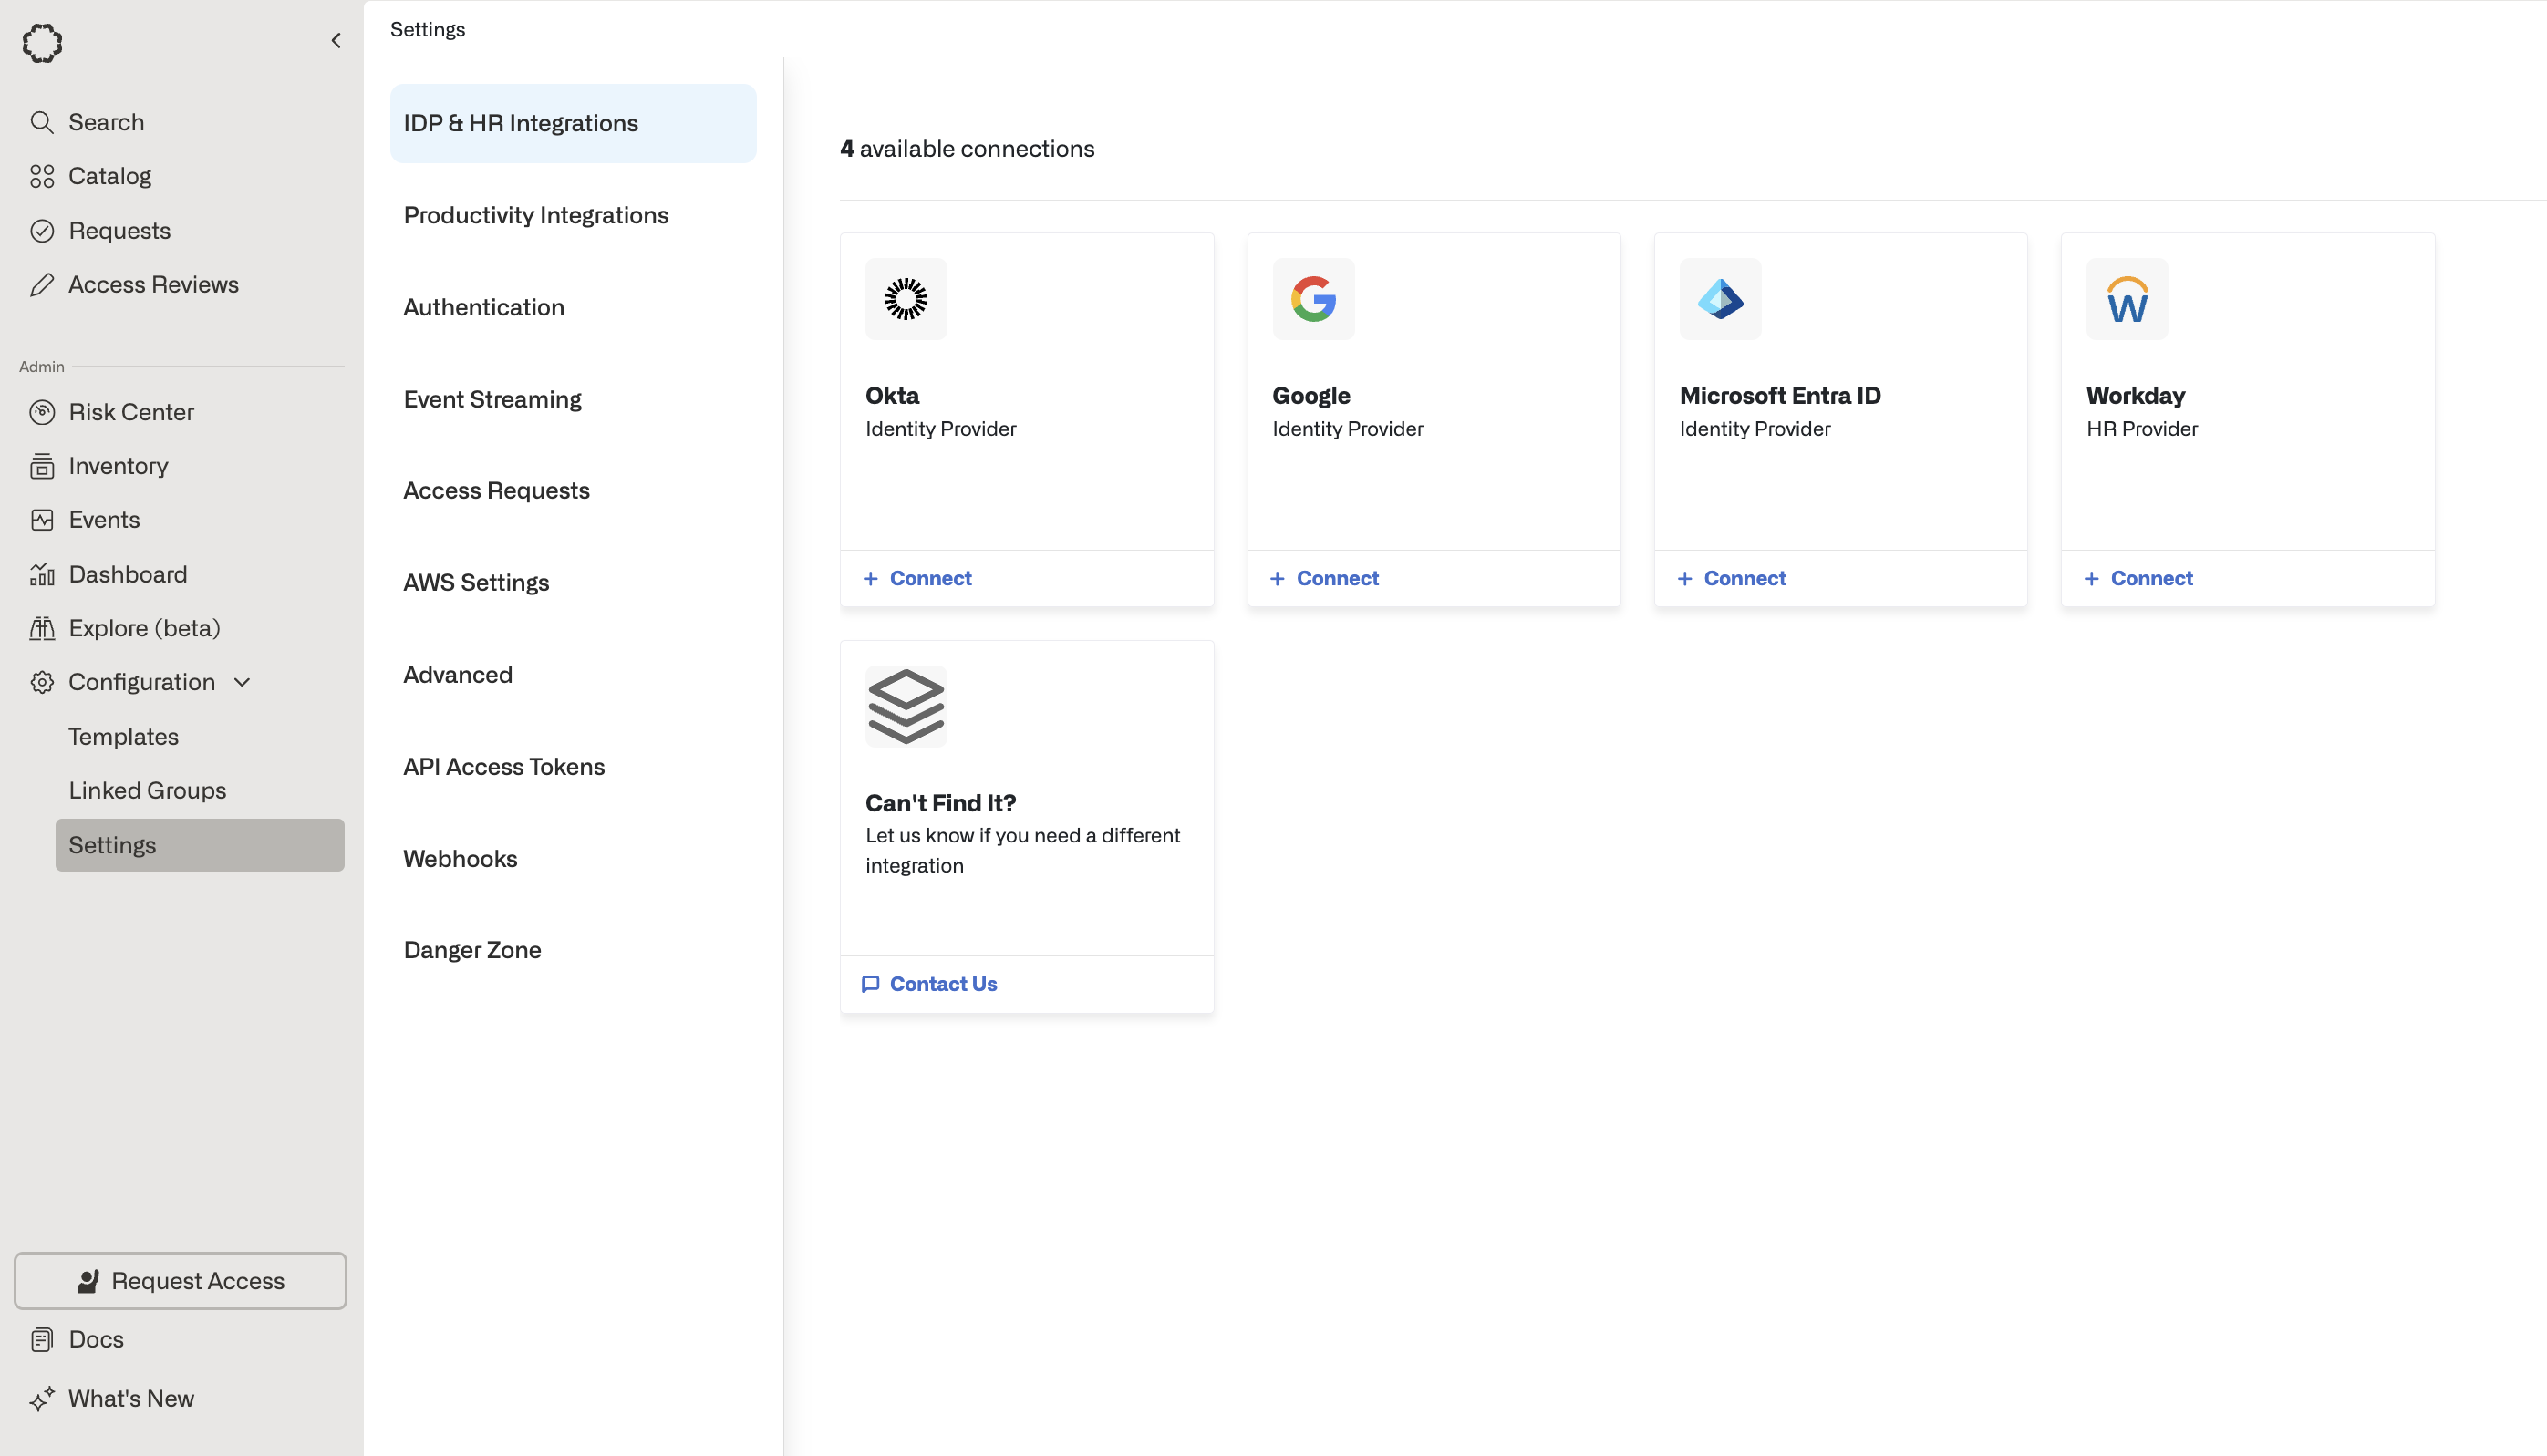
Learn how to configure Azure Entra as an IDP/HRIS Integration.
If your organization uses Azure Entra as an Identity Provider, you can additionally designate it as an IDP/HRIS Integration. This allows Opal to sync your Azure Entra identities and their attributes, on top of syncing and managing access to entitlements (e.g. Azure Entra Security Groups, Azure VMs, Azure DBs, etc).
Before you set up Azure Entra as your IDP, you must first create an Azure Entra App in Opal.Next, set up Azure Entra as your IDP using the following instructions:
Note: Opal only supports string type Custom Security Attributes.
Opal’s Azure app must have the CustomSecAttributeAssignment.ReadWrite.All application permission assigned.
Go to App Registrations.
In the sidebar, go to API Permissions and select Add a permission. Choose Microsoft Graph > Application Permissions and add CustomSecAttributeAssignment.ReadWrite.All
Opal tags should have the format <customAttributeSetName>.<attributeName>. ex. Student.IsFallIntern in order to properly match the Azure attributes. These are case-sensitive.
Last modified on November 5, 2025
Was this page helpful?
Assistant
Responses are generated using AI and may contain mistakes.