Using an API key instead of an OAuth client is deprecated. They are still supported but not recommended, as they have a maximum expiry of 90 days and must be refreshed manually.
To upgrade a Tailscale app that uses an API key, find the app in Inventory, then select Setup > Edit. Add the OAuth credentials and remove the API key. After you save the settings, check the App validations section to confirm your app authenticated correctly. No further action is needed after you add valid credentials.
In Opal, go to Inventory, click on the + App icon, and select Tailscale. Set the following fields.
Field
Value
Example(s)
App admin
The team that should manage the Tailscale app in Opal.
API Owners
Description
Let your end users know what they’re requesting access to.
SSH access to the production network
Tailnet name
Your tailnet’s domain name. Find this by opening the admin console and copying the name next to the Tailscale logo in the upper left.
example.com, [email protected], example.github
Tailscale OAuth Client ID
The Client ID of the OAuth client you generated in Step 1.
Tailscale OAuth Client Secret
The Client secret of the OAuth client you generated in Step 1.
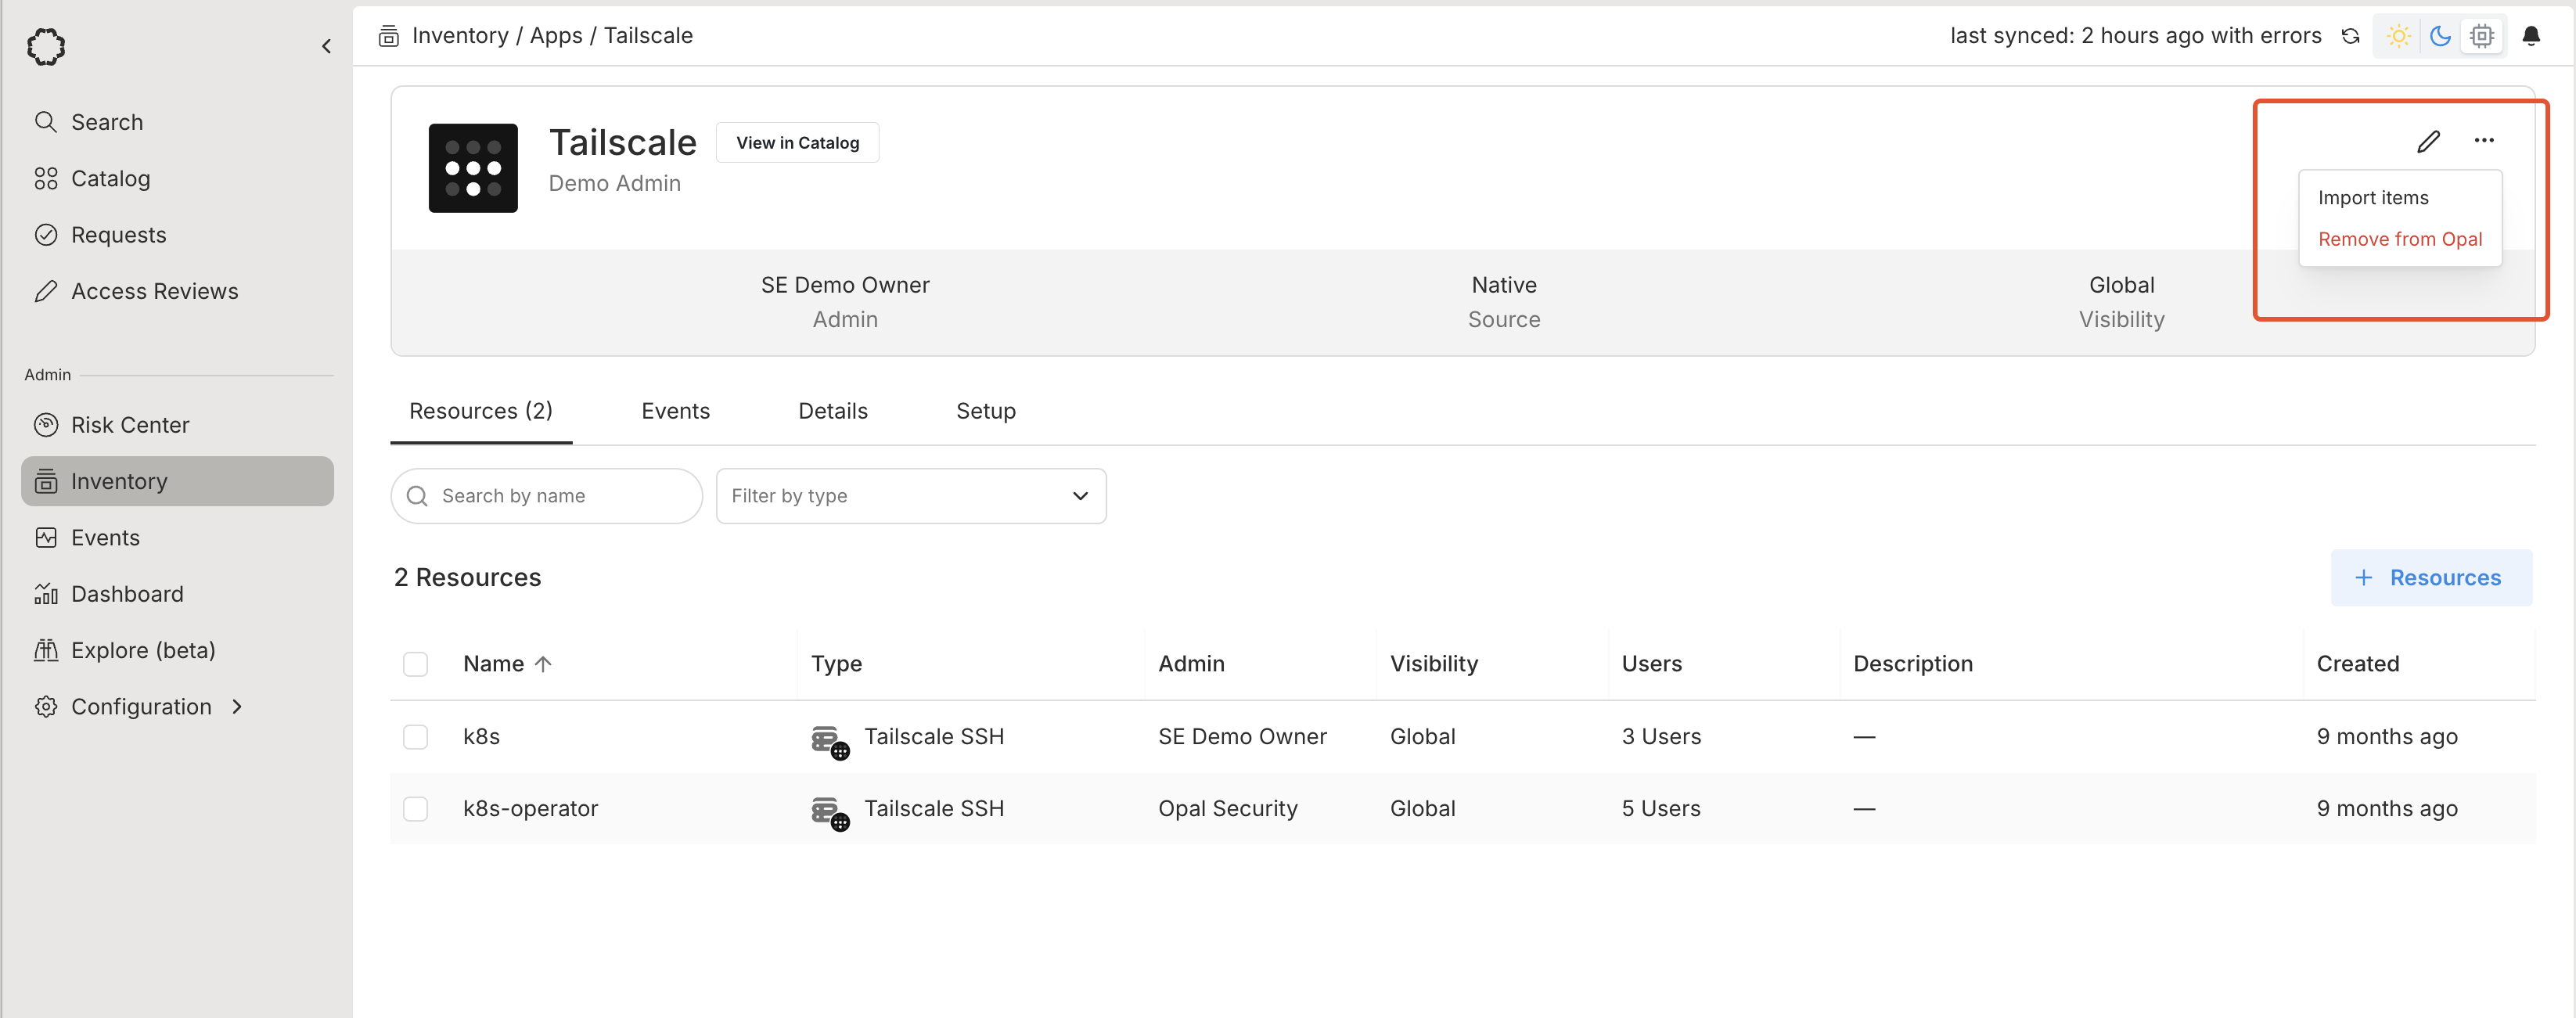
Import Tailscale resources to Opal by selecting … > Import items.
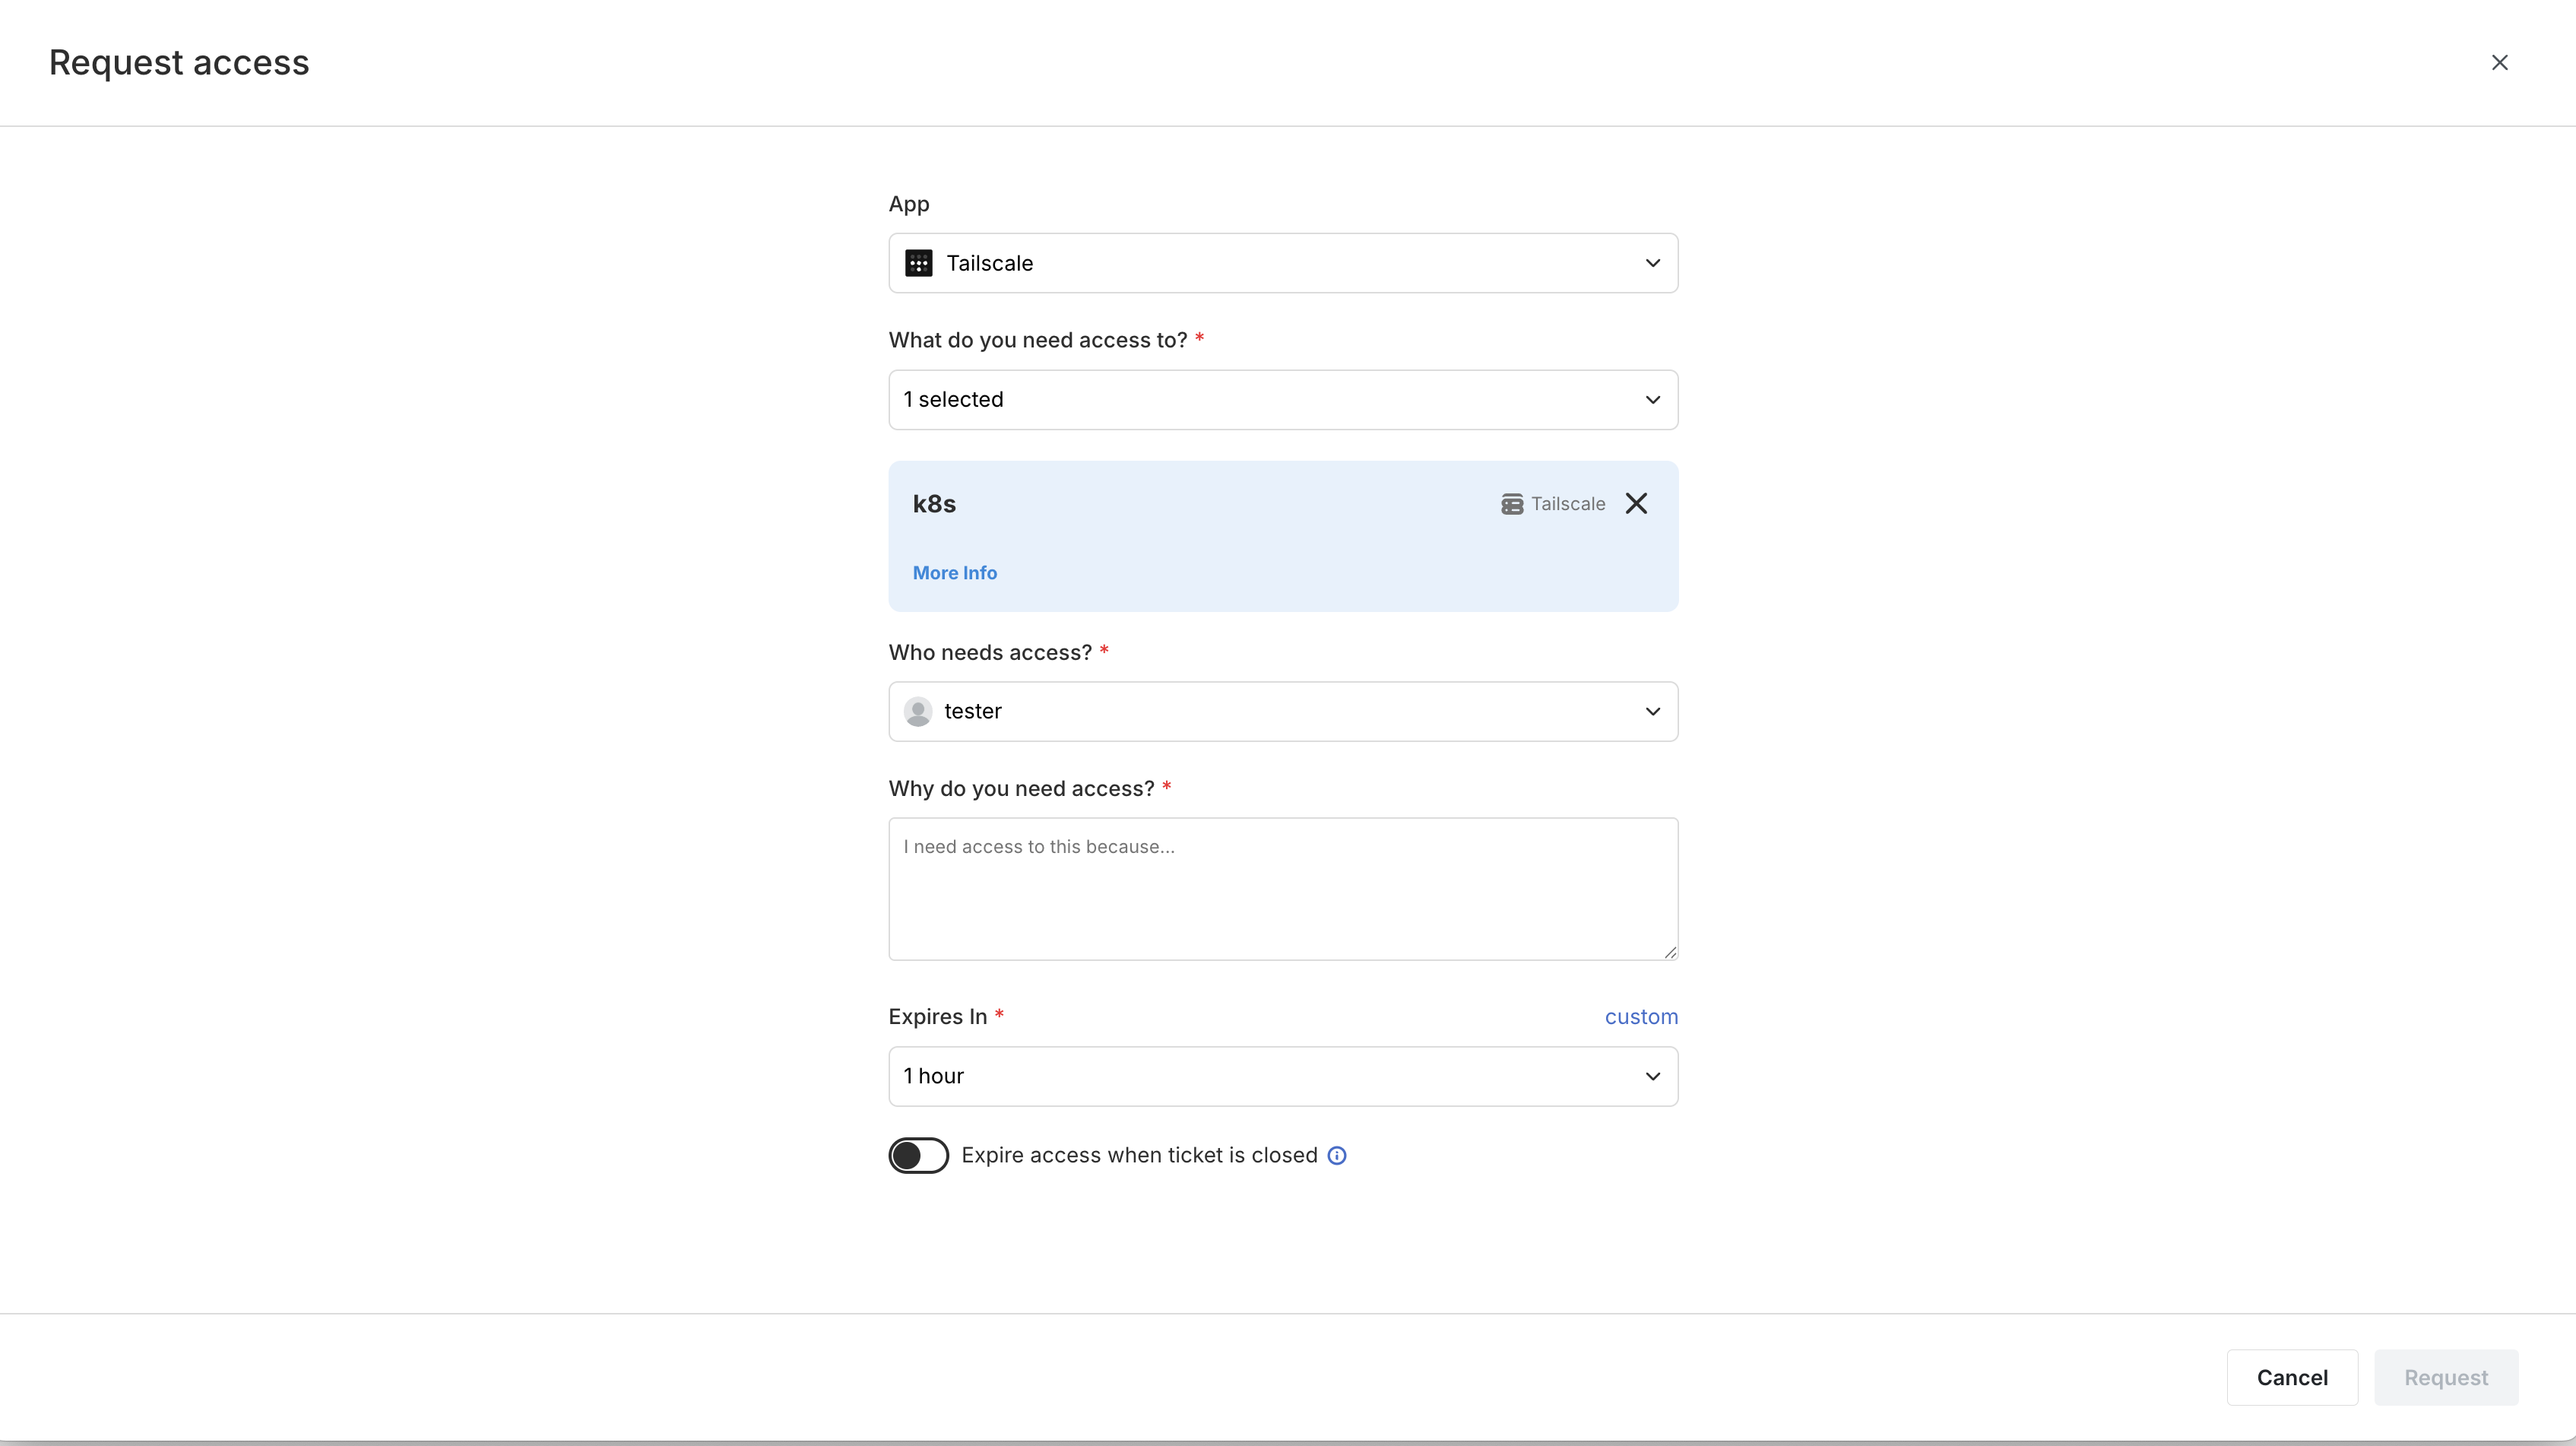
For each ACL tag that is selected, Opal automatically parses the existing access rules and SSH access rules that apply to that tag, and which groups have access to the tagged sources using those rules.Users can now request access or SSH access to a specific tag in Tailscale or to join a specific group.
Last modified on November 5, 2025
Was this page helpful?
Assistant
Responses are generated using AI and may contain mistakes.