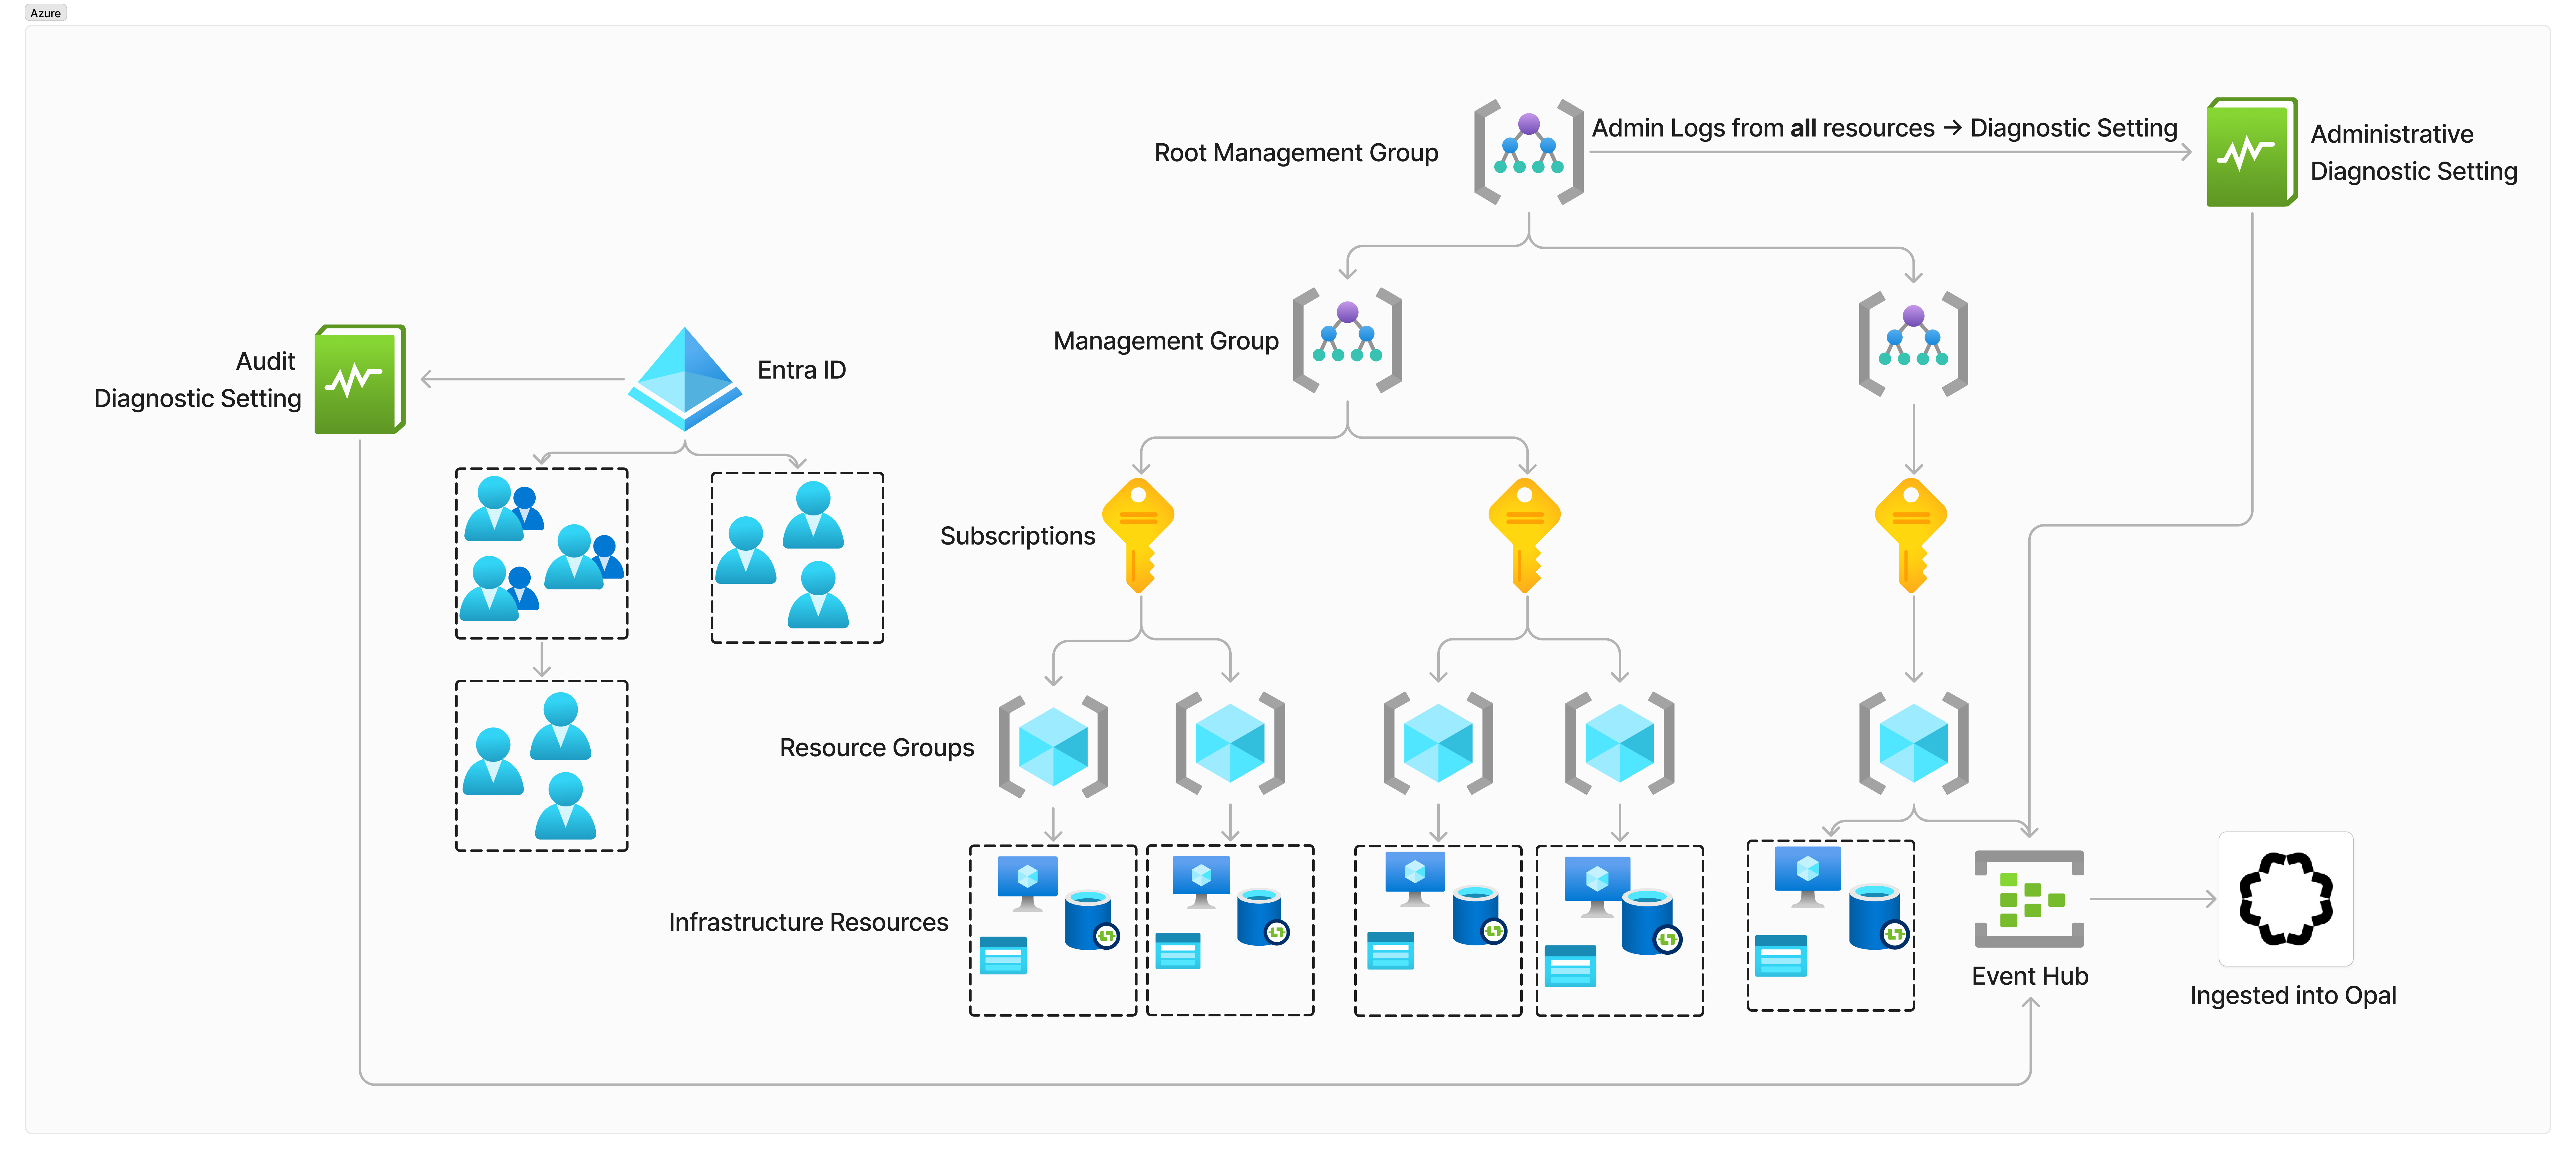
With Opal Real Time Sync, admins can see access changes to an application’s Resources and Groups in near real-time and on an event-driven basis. Instead of waiting for Opal’s scheduled syncs, each time an access change event occurs in the remote system (e.g. User added to a Group), Opal automatically syncs and reflect that change.If you use Opal’s Azure (Entra) Integration, you can expect to see changes in Opal as quickly as 3 minutes and no later than 10 minutes once you set up this feature.
The Azure CLI configured. If you have not already, follow the instructions below.
Follow the instructions hereto install the Azure CLI
Follow the instructions here to log in to the Azure CLI
An Azure Subscription
The following providers must be registered in the Azure Subscription. If they are not registered, do so using: az provider register --namespace <resource-provider-namespace> --subscription <subscription_id>
Microsoft.Insights
Microsoft.EventHub
Administrative access to an Azure Subscription, specifically the permissions listed below.
2. Create a diagnostic setting at the root management group
For this step, we will need to use the Azure REST API, as this functionality is not available anywhere else. You can trigger this using any REST client you prefer. An authorization token is required, which you can retrieve from the Azure CLI using the following command:
az account get-access-token --query accessToken --output tsv
To create the diagnostic setting, fill in the following fields in the command below.
<root-management-group-ID>: The root management group for your Azure directory
<diagnostic-setting-name>: Any name
<event-hub-subscription>: The subscription under which you created your event hub namespace
<event-hub-resource-group>: The resource group under which you created your event hub namespace
<event-hub-namespace-name>: The name of your event hub namespace
<authorization-rule-name>: The name of the authorization rule configured above
<event-hub-name>: The name of the event hub configured above
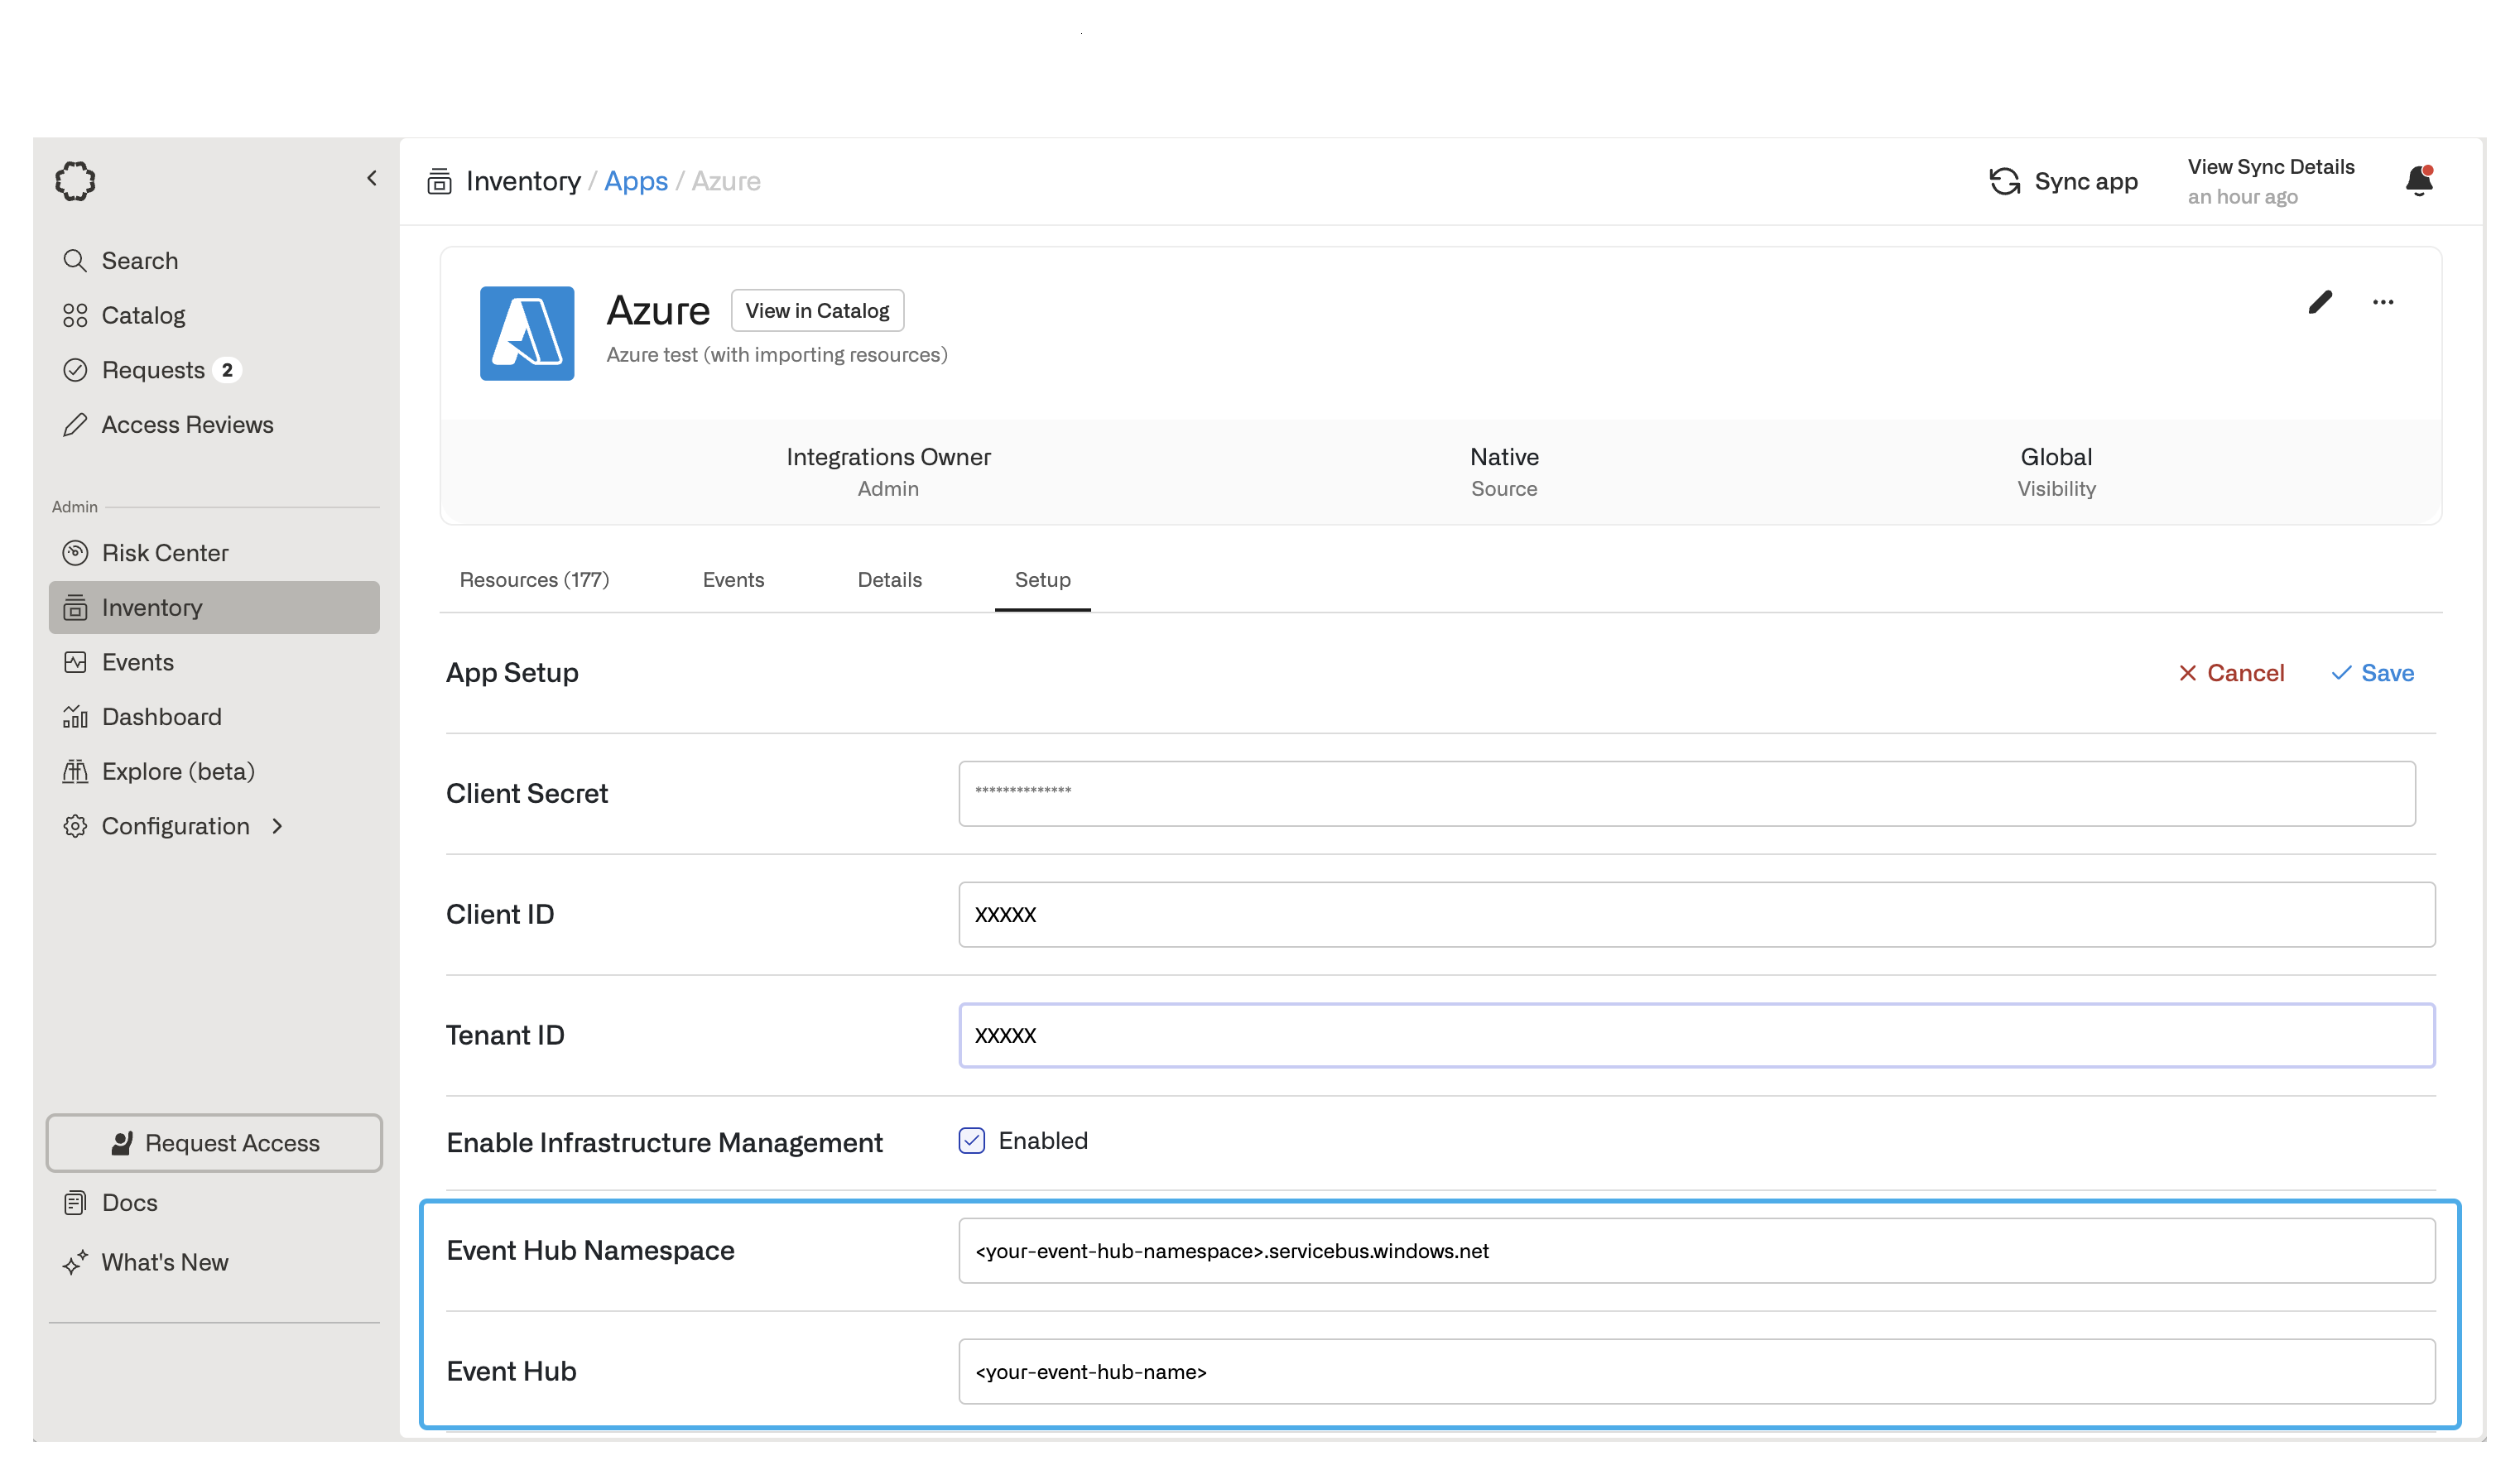
Go to your Azure app in Opal, select Setup, and click Edit to configure your event hub:
Event Hub Namespace: This must be the fully-qualified name of your event hub namespace. It will be of the form <your-event-hub-namespace-name>.servicebus.windows.net
Event Hub Name: Your event hub’s name, as returned from the terraform apply.
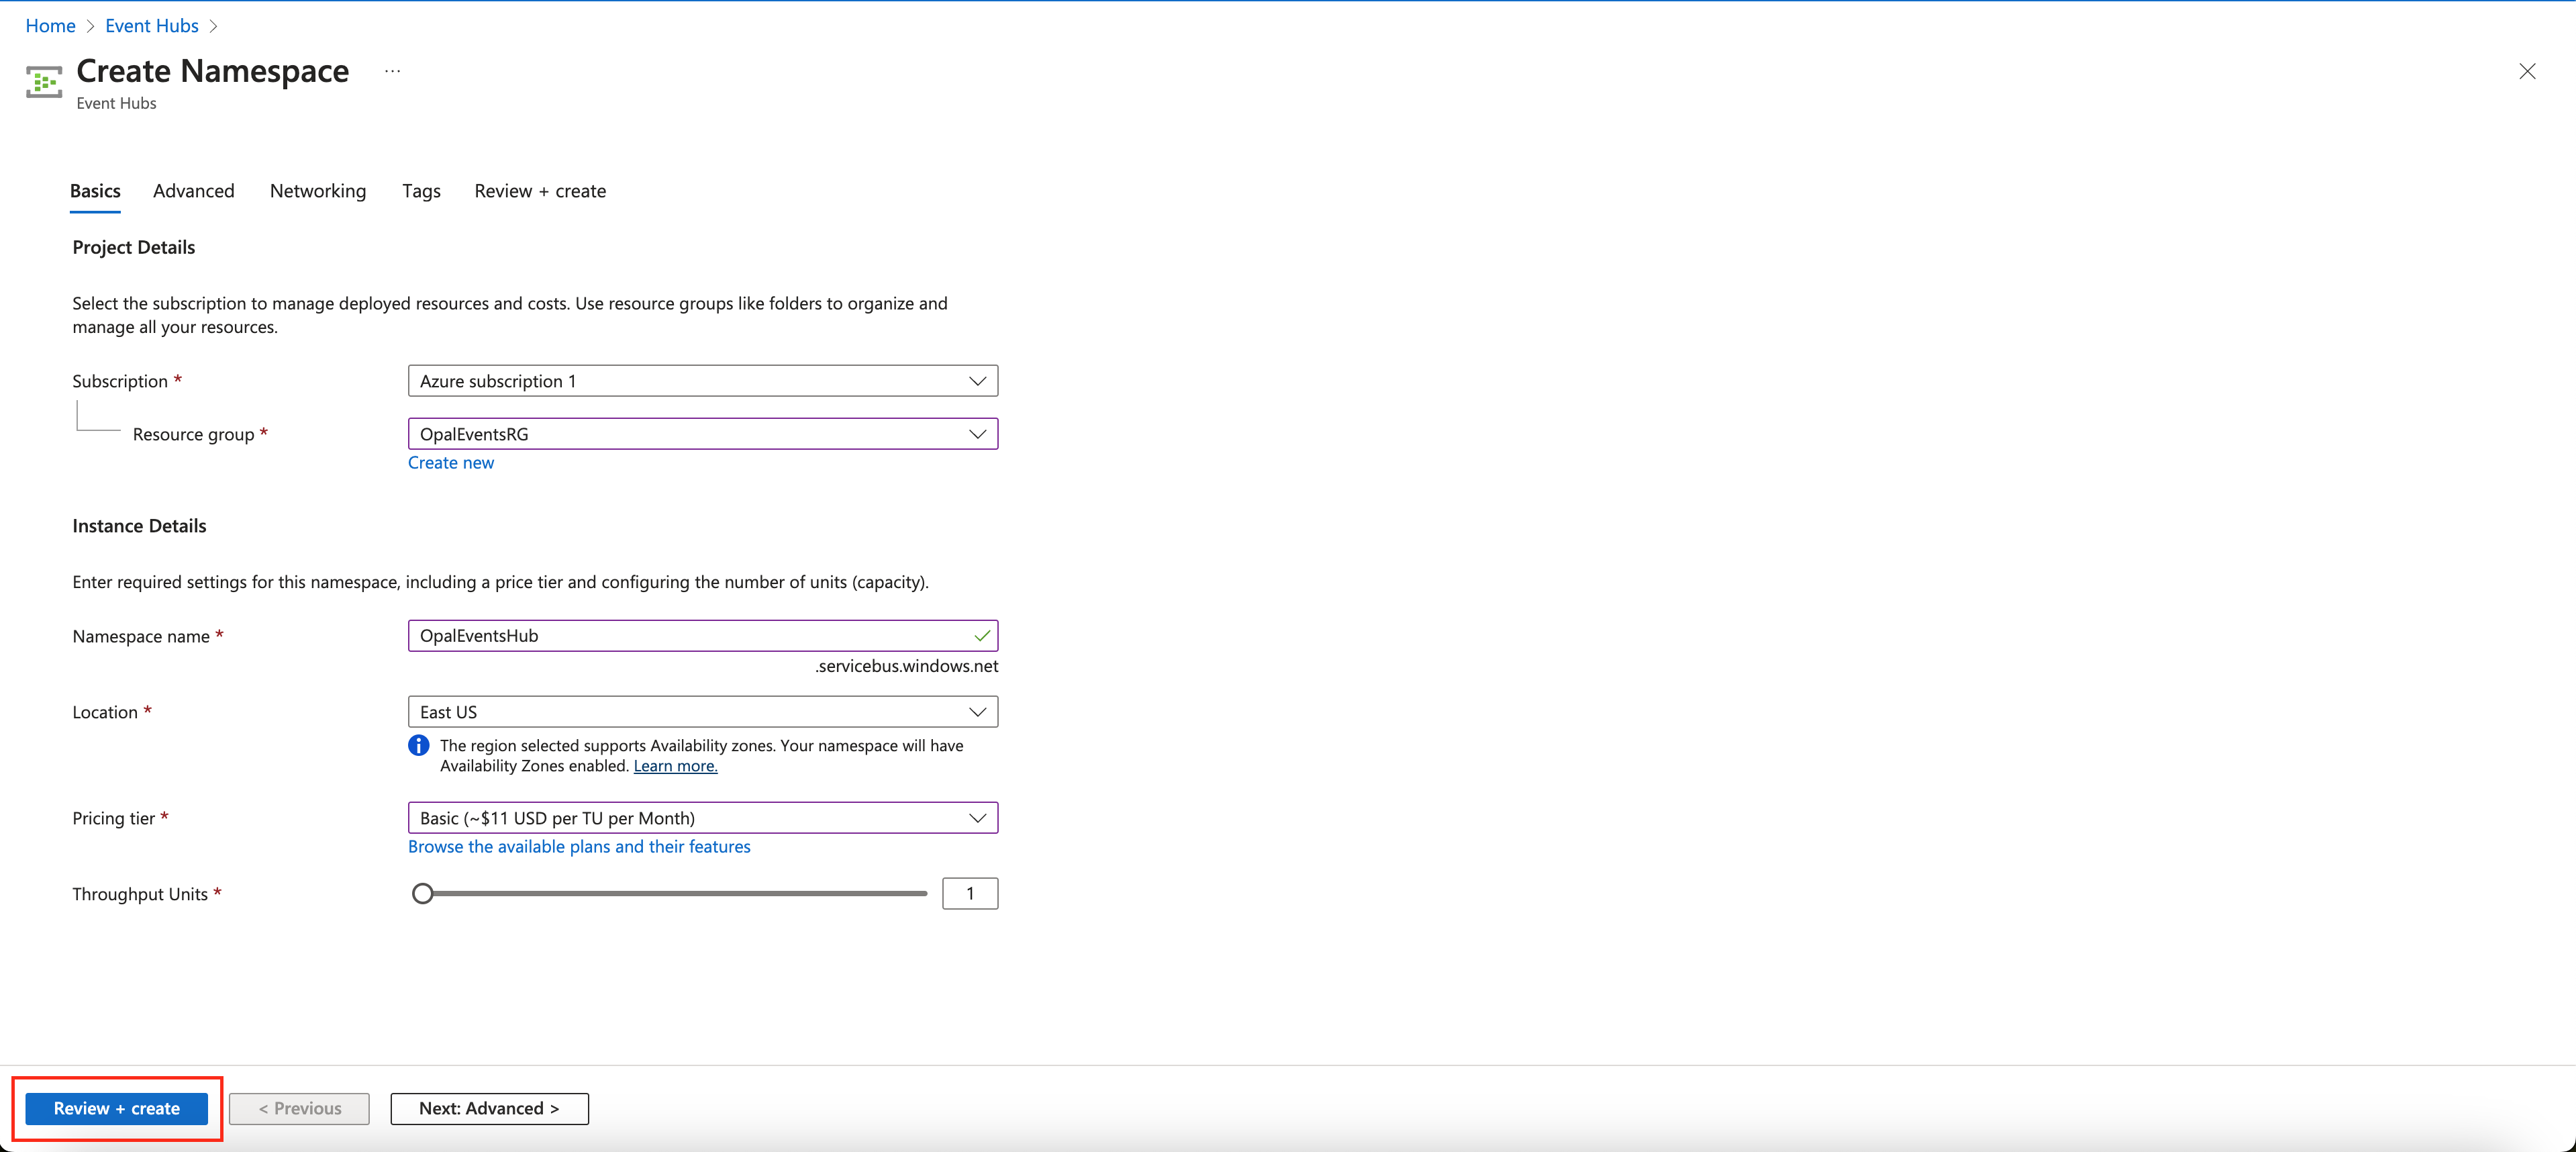
Under the following steps, you can configure any other setup required by your use-case. No further configuration for the event hub namespace is required for integration with Opal. Click “Review + create”Once created, your event hub will take a few minutes to deploy.
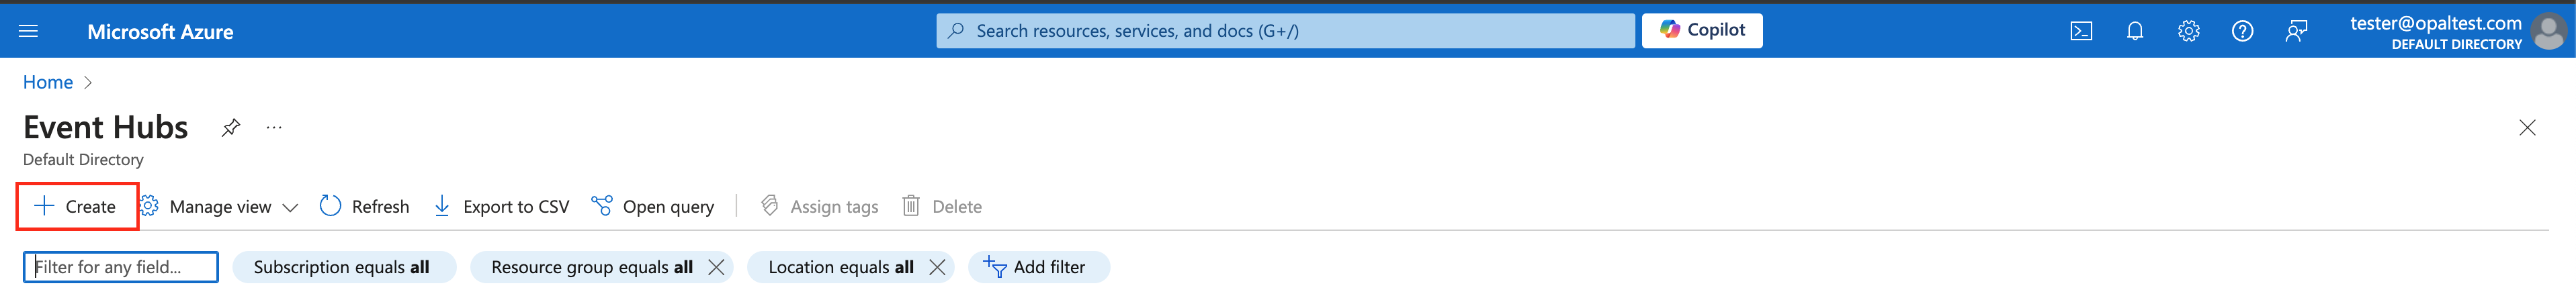
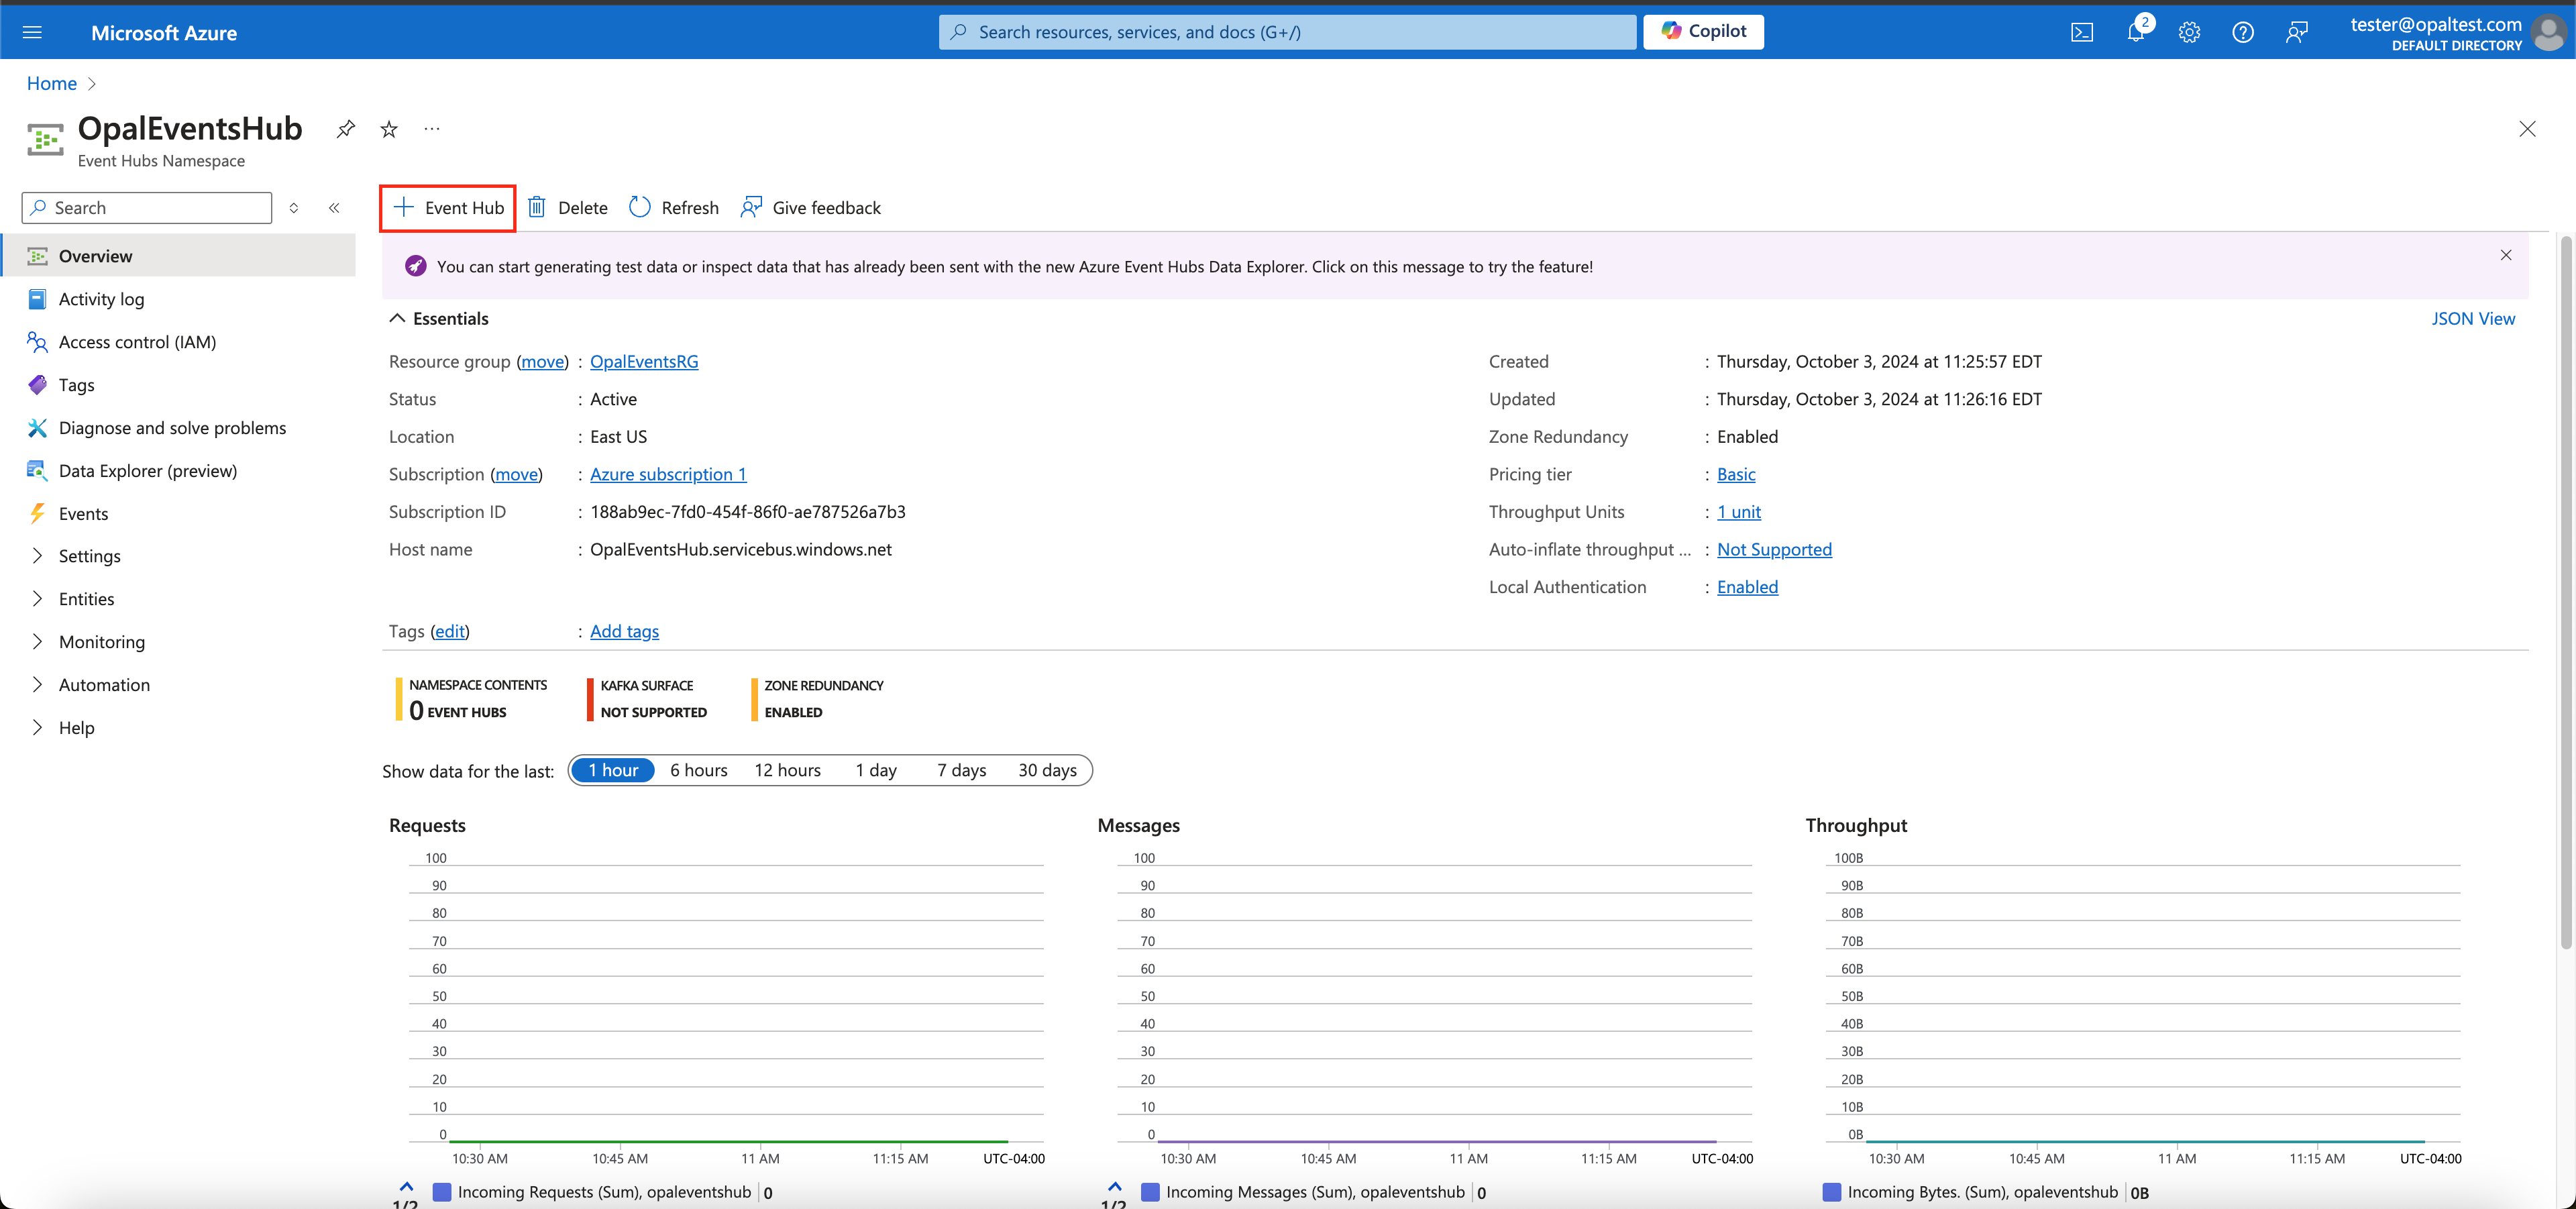
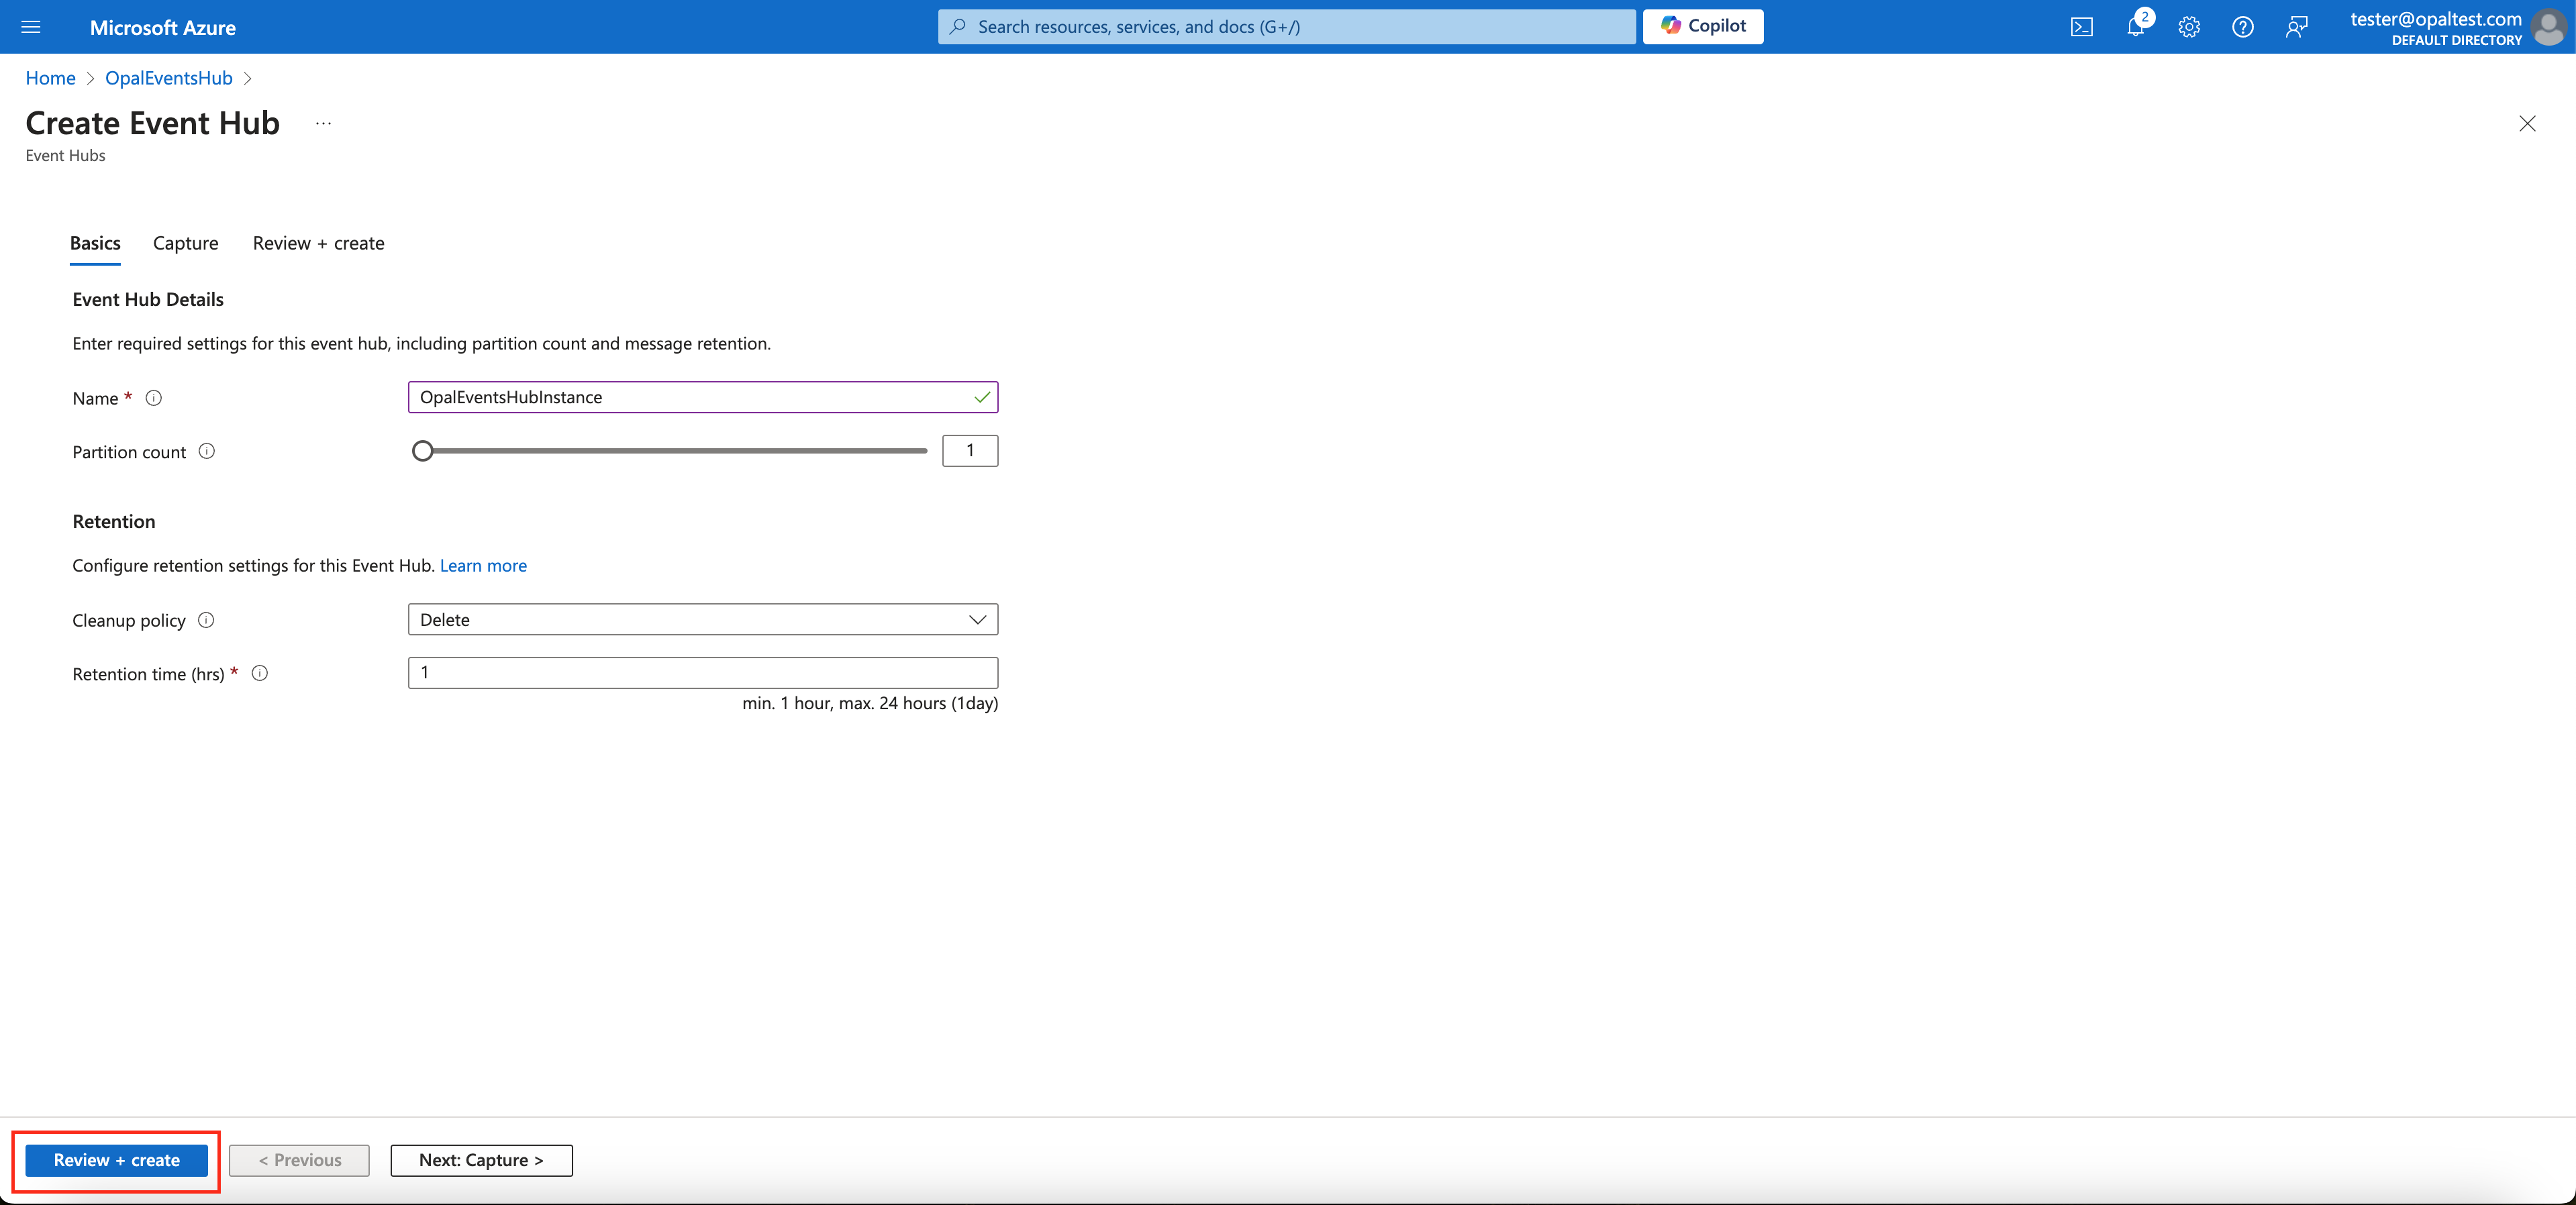
Once your event hub namespace is deployed, go to it in the Azure UI and click + Event Hub.On the first page, you will be prompted to configure the following:
Name
Partition Count: We recommend setting the partition count to 1
Cleanup Policy: Controls what happens when events reach their retention limit. We recommend using Delete
Retention Time: The maximum retention period available to you will differ based on the pricing tier you chose in step 1. We recommend using the longest retention period possible.
On the Capture tab, if you have a premium-tier namespace, you can enable capturing the data that is streamed by your event hub in Azure Data Lake or Azure Blob Storage. We recommend you keep this off.Once complete, click Review + Create, confirm your configuration and create your event hub.
Authorization rules allow Azure to push audit and administrative logs to your event hub, see here for more details. Fill in the following fields in the command below to create an authorization rule on your namespace
<authorization-rule-name>: Can be any name
<event-hub-namespace-name>: Name of the event hub namespace configured above
<event-hub-resource-group>: Resource group under which the event hub namespace was created
4. Create a diagnostic setting at the root management group
For this step, we will need to use the Azure REST API. You can trigger this via any REST client you would like. An authorization token is required, which you can retrieve from the Azure CLI using the following command:
az account get-access-token --query accessToken --output tsv
To create the diagnostic setting, fill in the following fields in the command below to create a diagnostic setting
<root-management-group-ID>: The root management group for your Azure directory
<diagnostic-setting-name>: Any name
<event-hub-subscription>: The subscription under which you created your event hub namespace
<event-hub-resource-group>: The resource group under which you created your event hub namespace
<event-hub-namespace-name>: The name of your event hub namespace
<authorization-rule-name>: The name of the authorization rule configured above
<event-hub-name>: The name of the event hub configured above
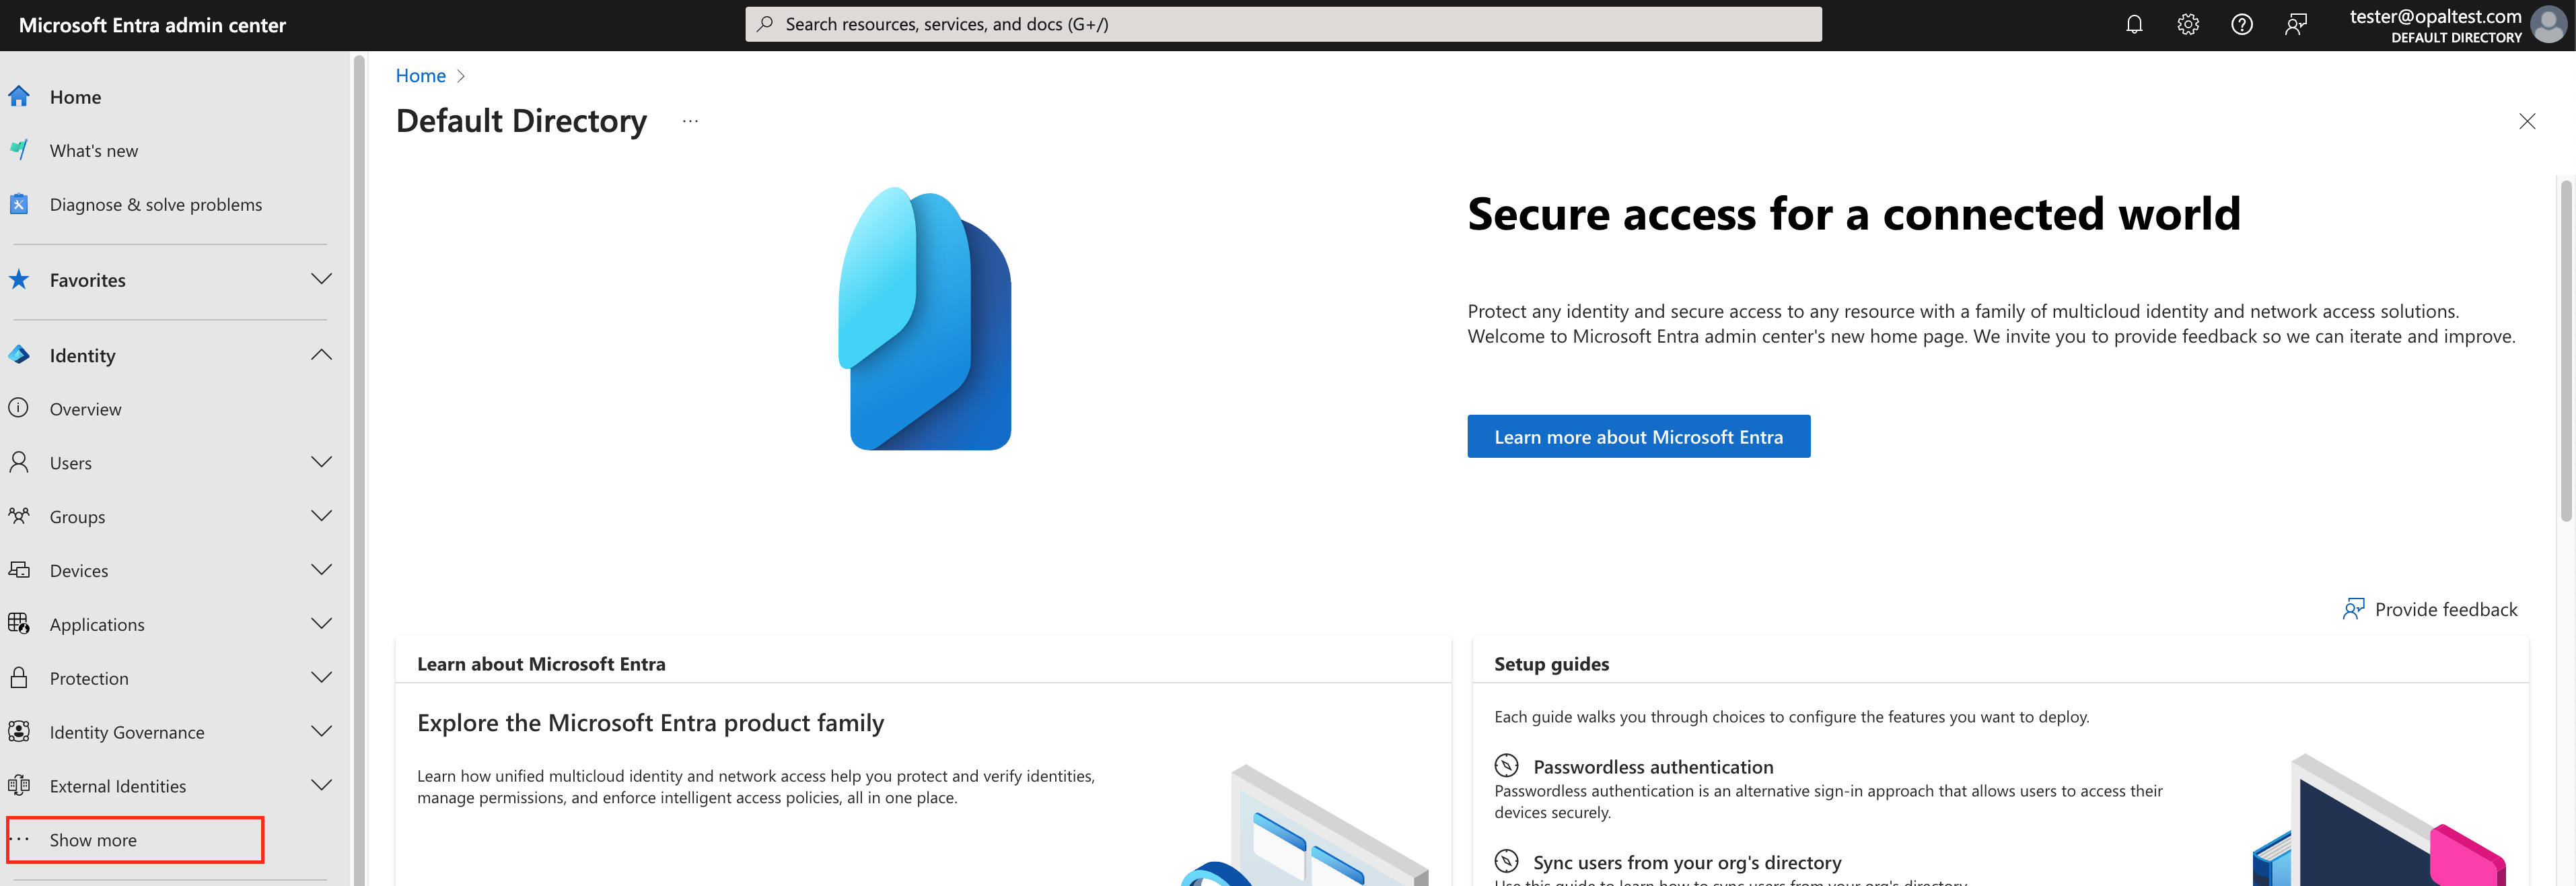
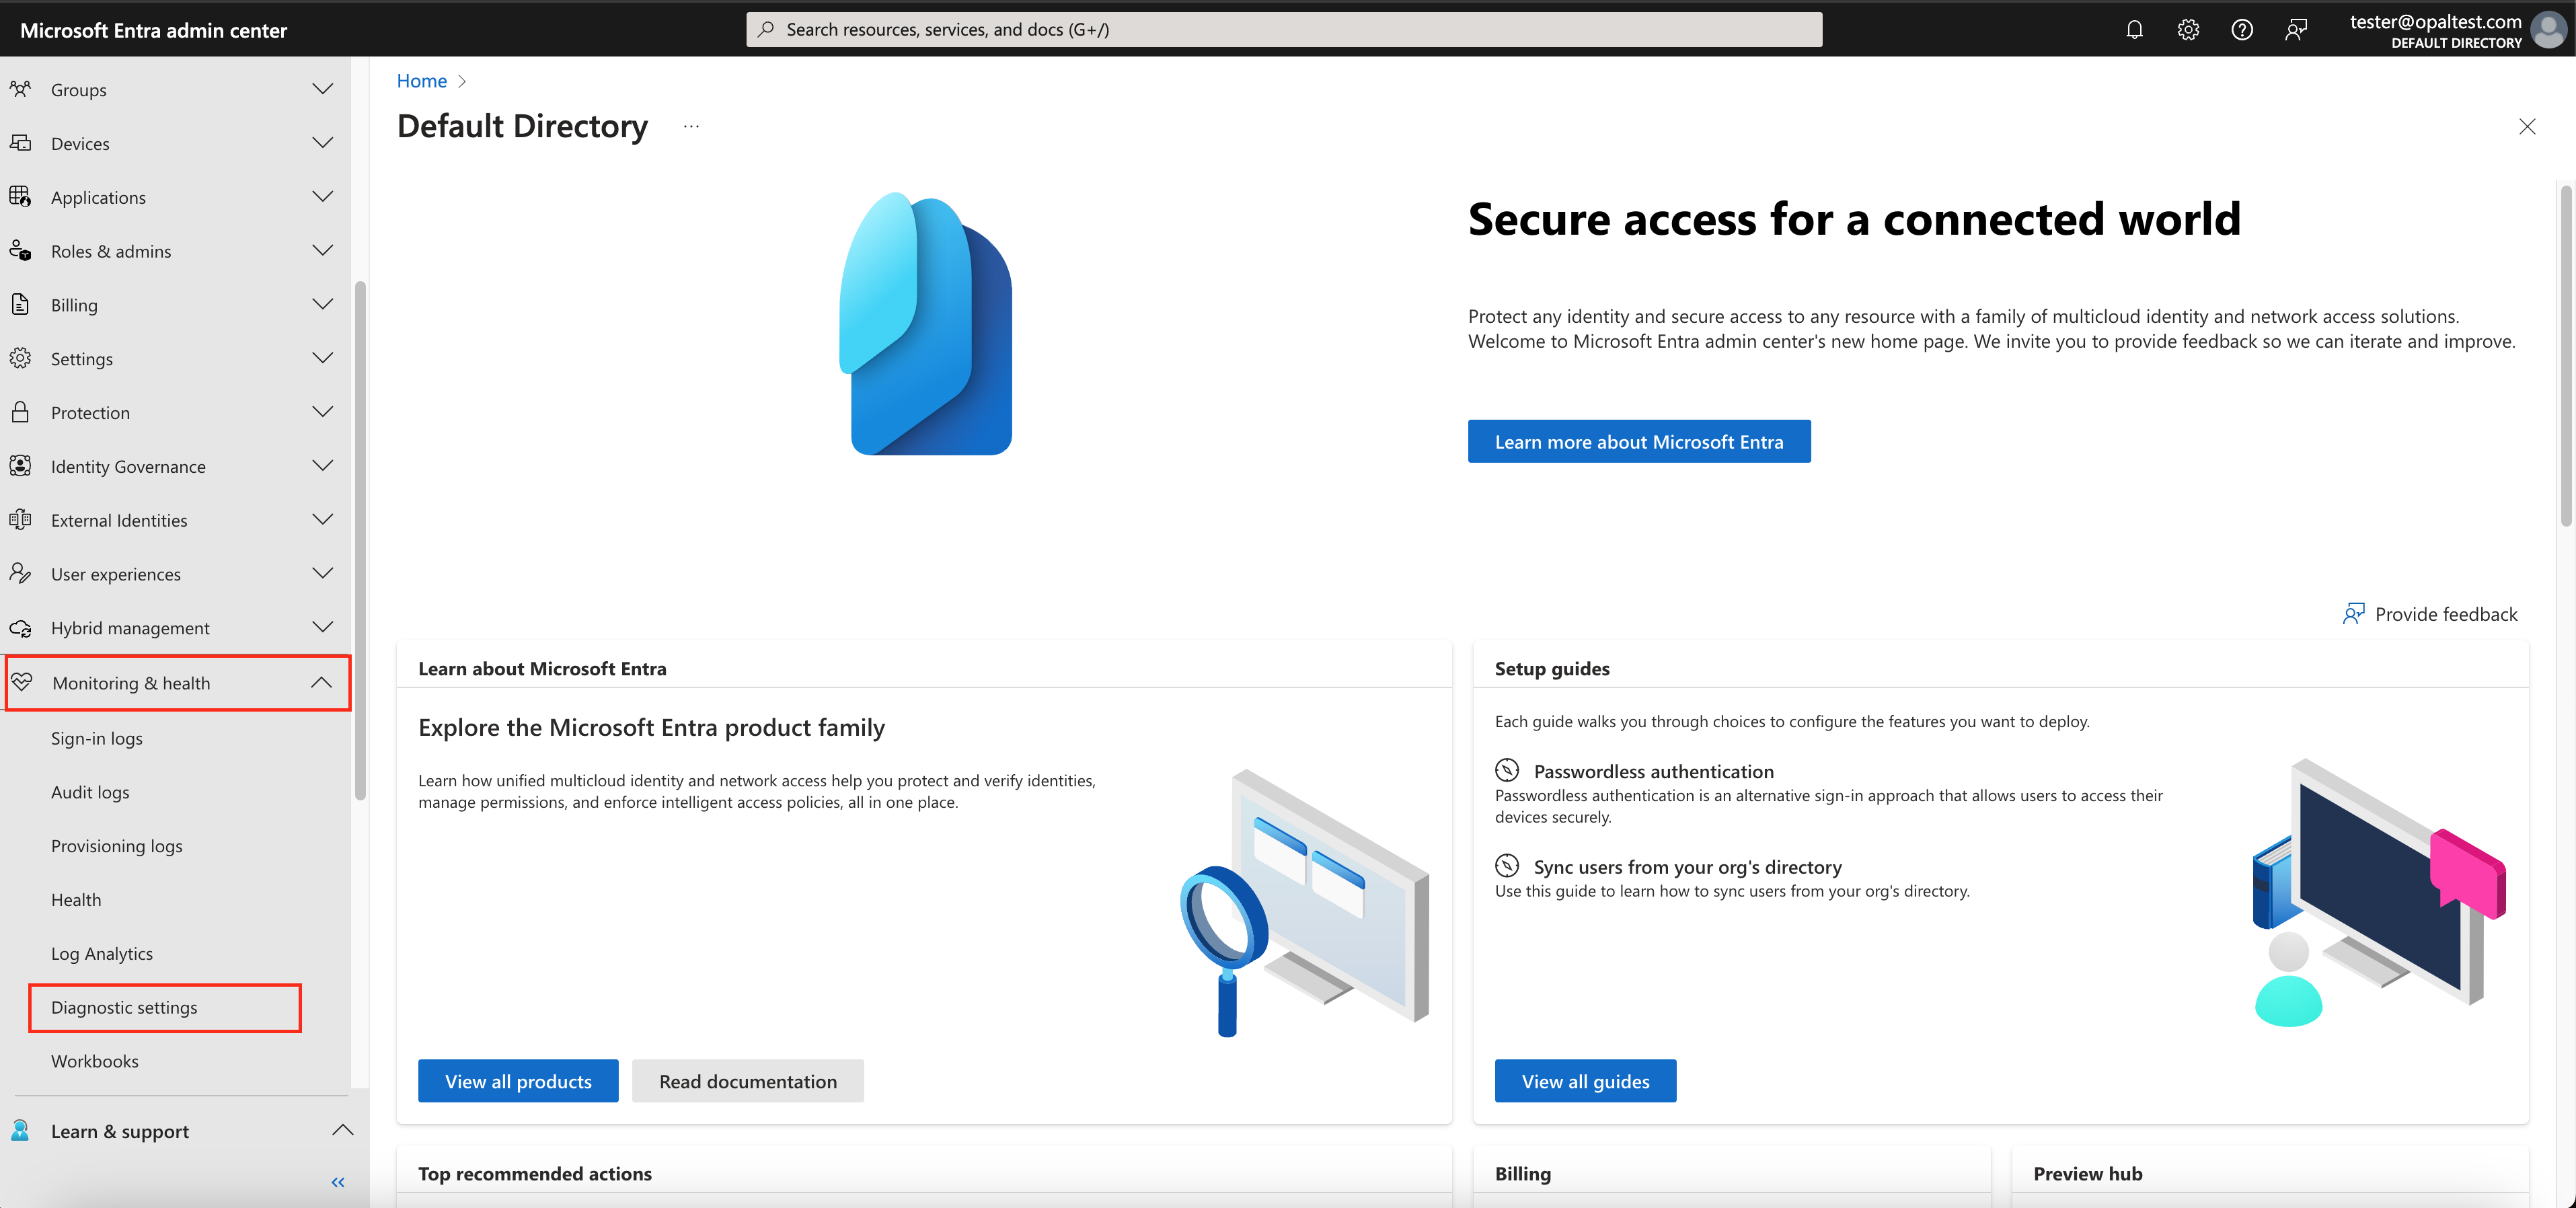
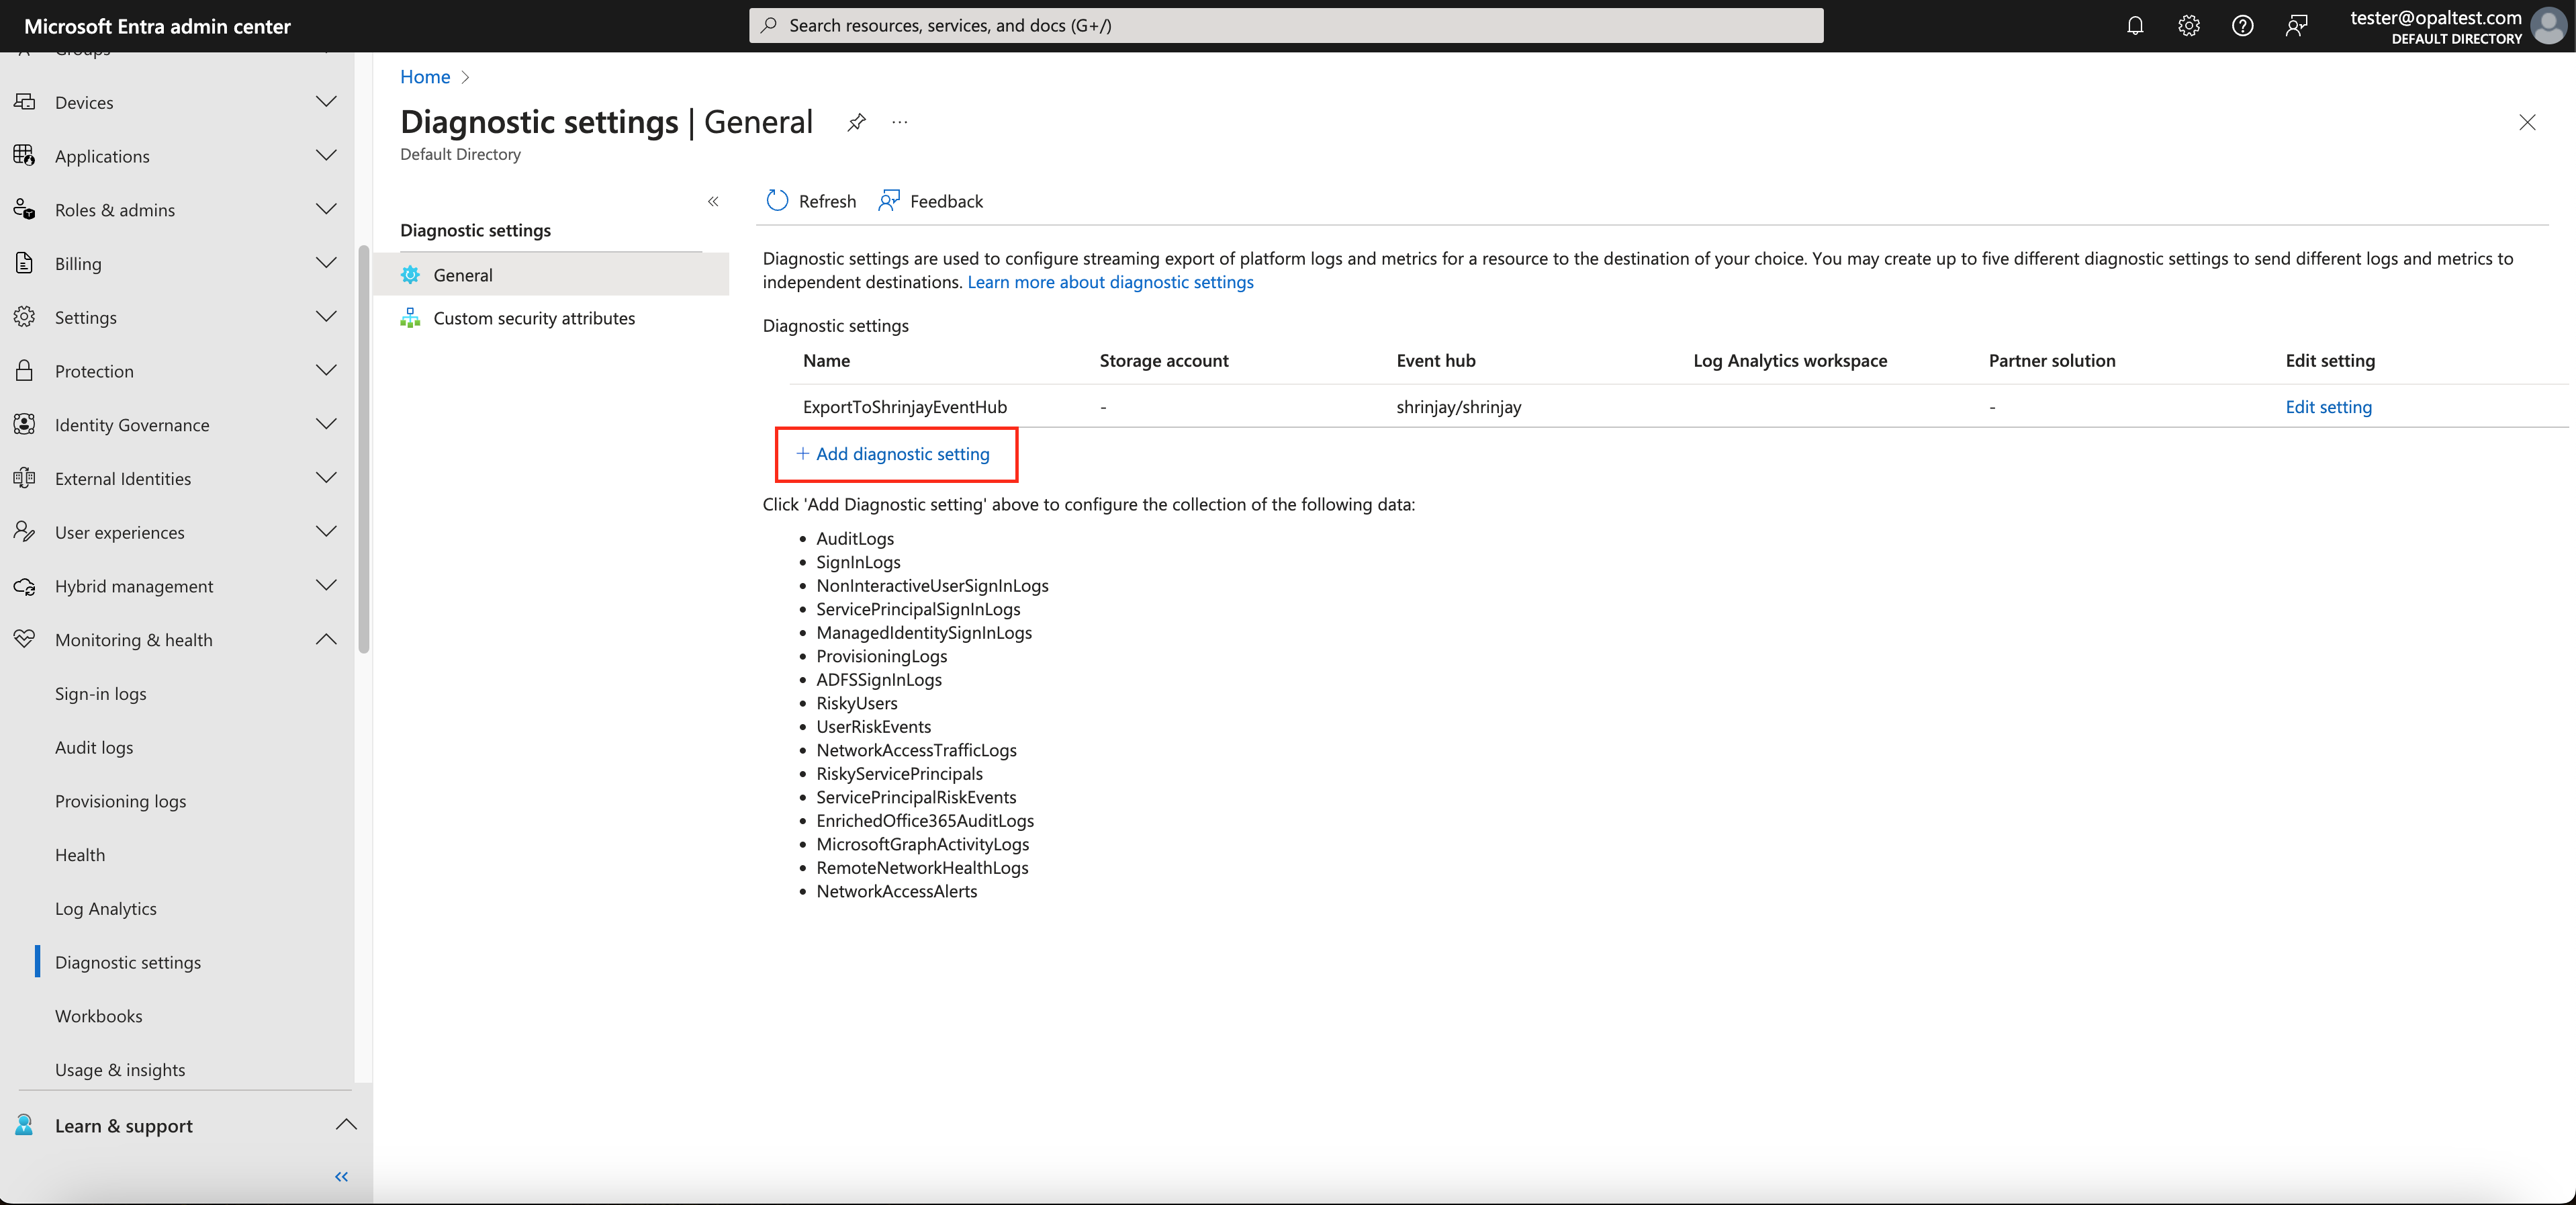
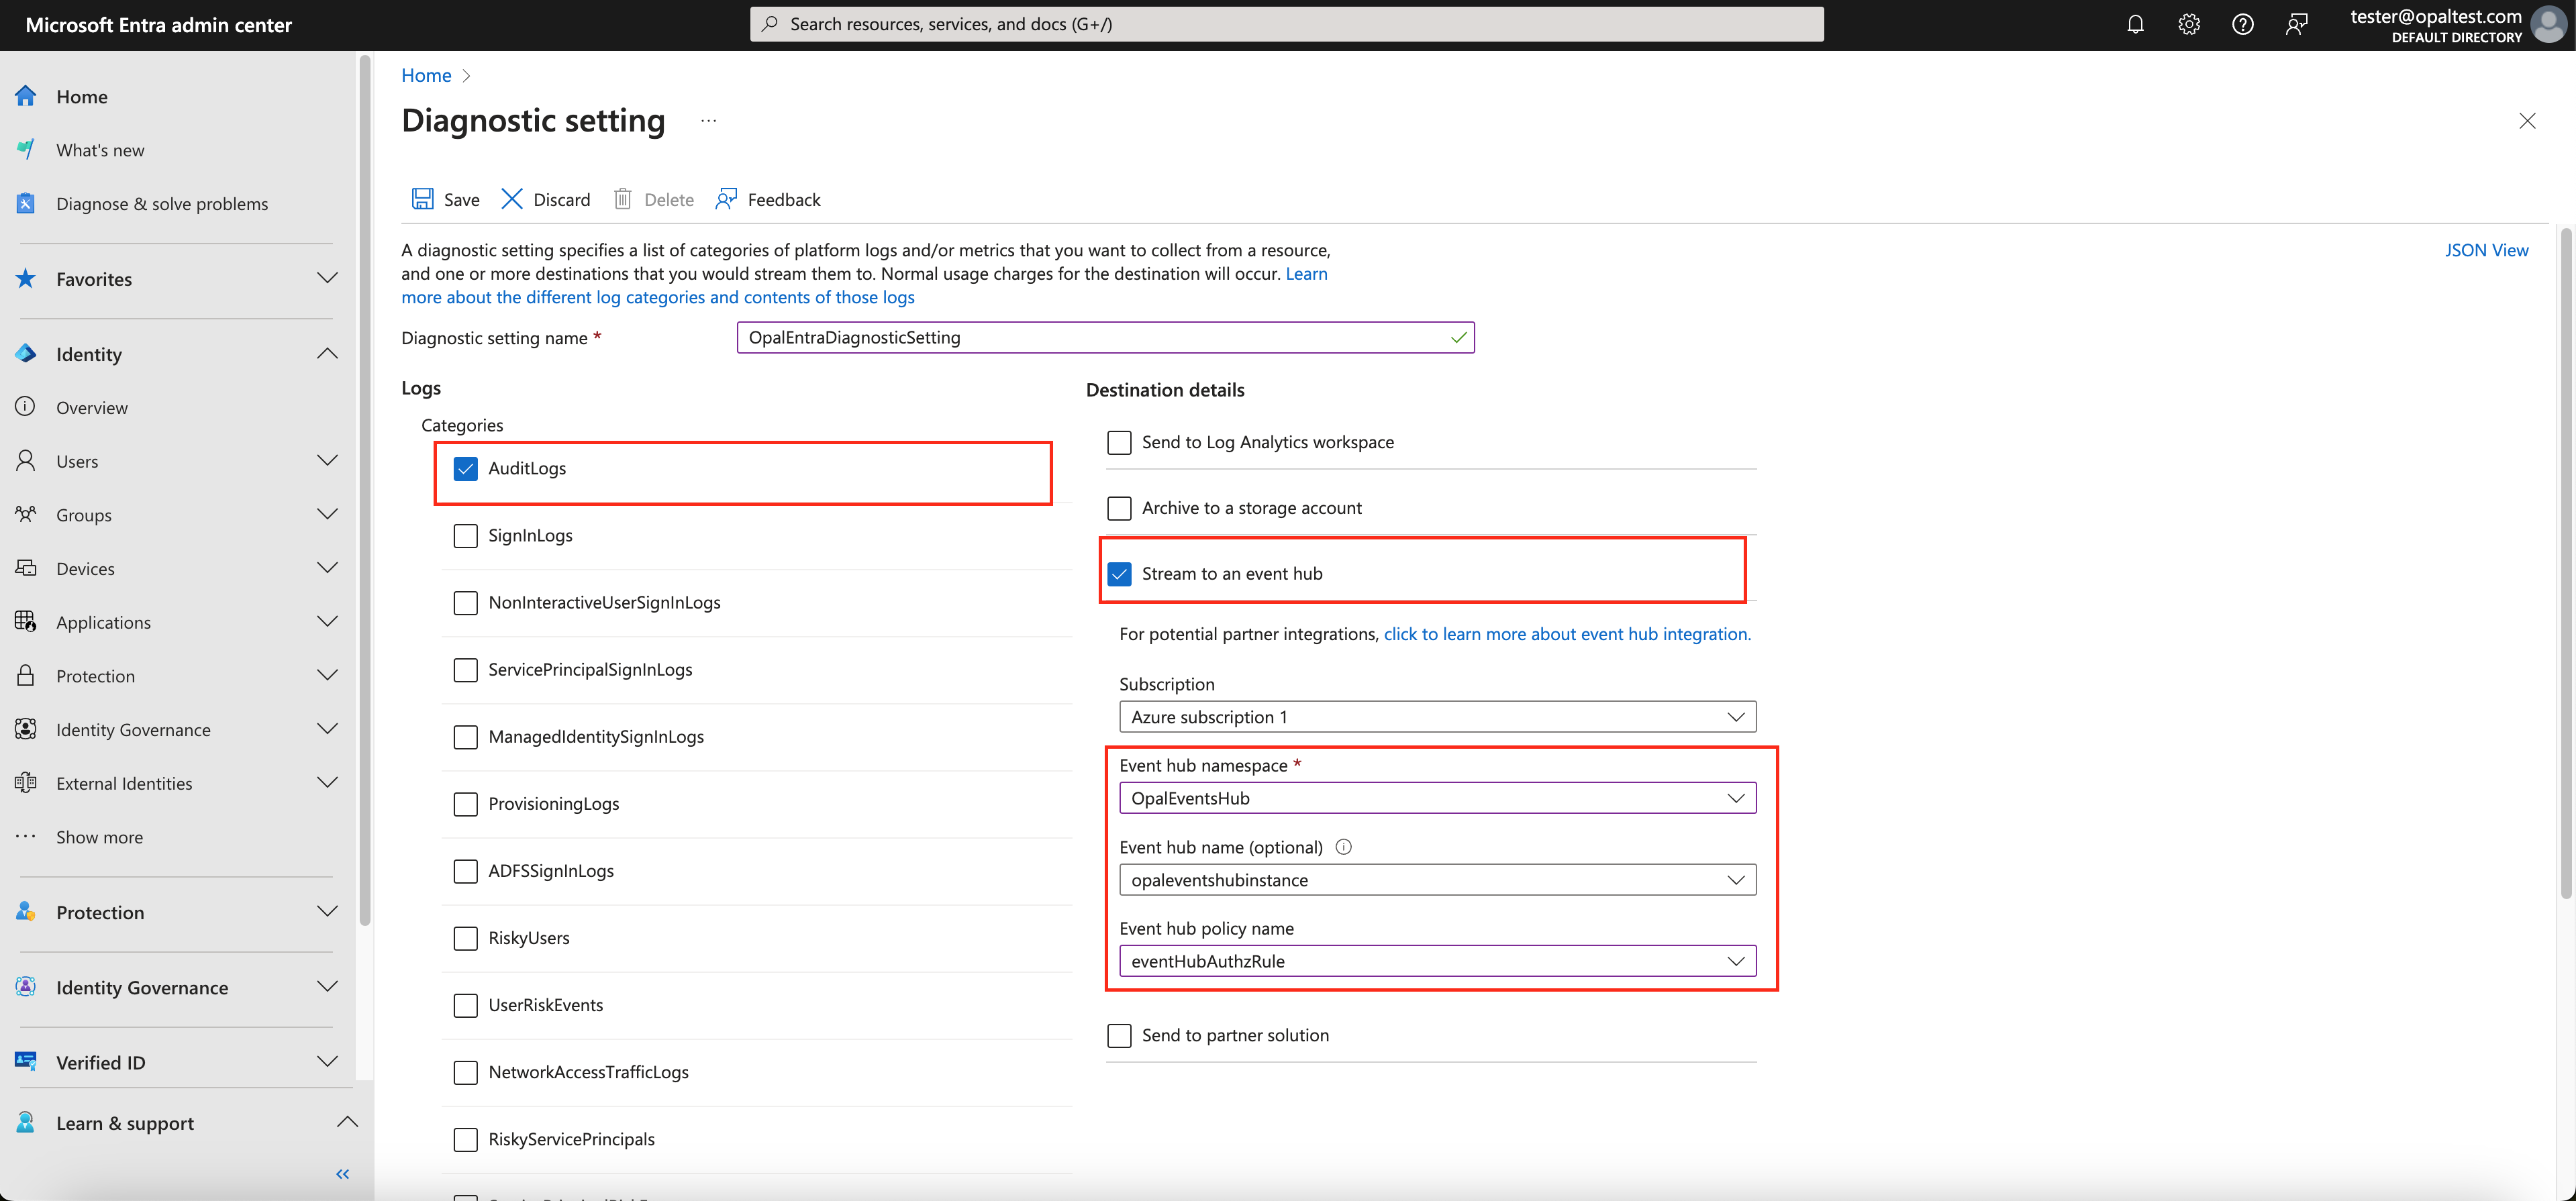
Go to Microsoft Entra and click Show More on the left hand bar.Expand Monitoring & health and select Diagnostic settings.Select Add diagnostic setting.You will be prompted to configure the following:
Diagnostic setting name
Log Categories: Select AuditLogs
Destination details: Select Stream to an event hub
Select the subscription, event hub namespace, event hub and authorization rule created above
Go to your Azure app in Opal, select Setup and click Edit to configure your event hub:
Event Hub Namespace: This must be the fully-qualified name of your event hub namespace. It will be of the form <your-event-hub-namespace-name>.servicebus.windows.net
Event Hub Name: Your event hub’s name
Last modified on October 28, 2025
Was this page helpful?
Assistant
Responses are generated using AI and may contain mistakes.